
Last updated: 2026-10-09
What Is the Cyber Resilience Act?
The Cyber Resilience Act (CRA) is Regulation (EU) 2024/2847. It entered into force on 10 December 2024 and establishes binding cybersecurity requirements for products with digital elements made available on the EU market in the course of a commercial activity, whether for payment or free of charge, whose intended purpose or foreseeable use includes a data connection to a device or network. Obligations apply to manufacturers, importers and distributors according to their role.
In short: anyone who markets software, hardware, or network-connected products in the EU must be able to demonstrate cybersecurity as part of the product from the start. Use our Scope Check to find out whether your product is affected.
The Three Application Dates
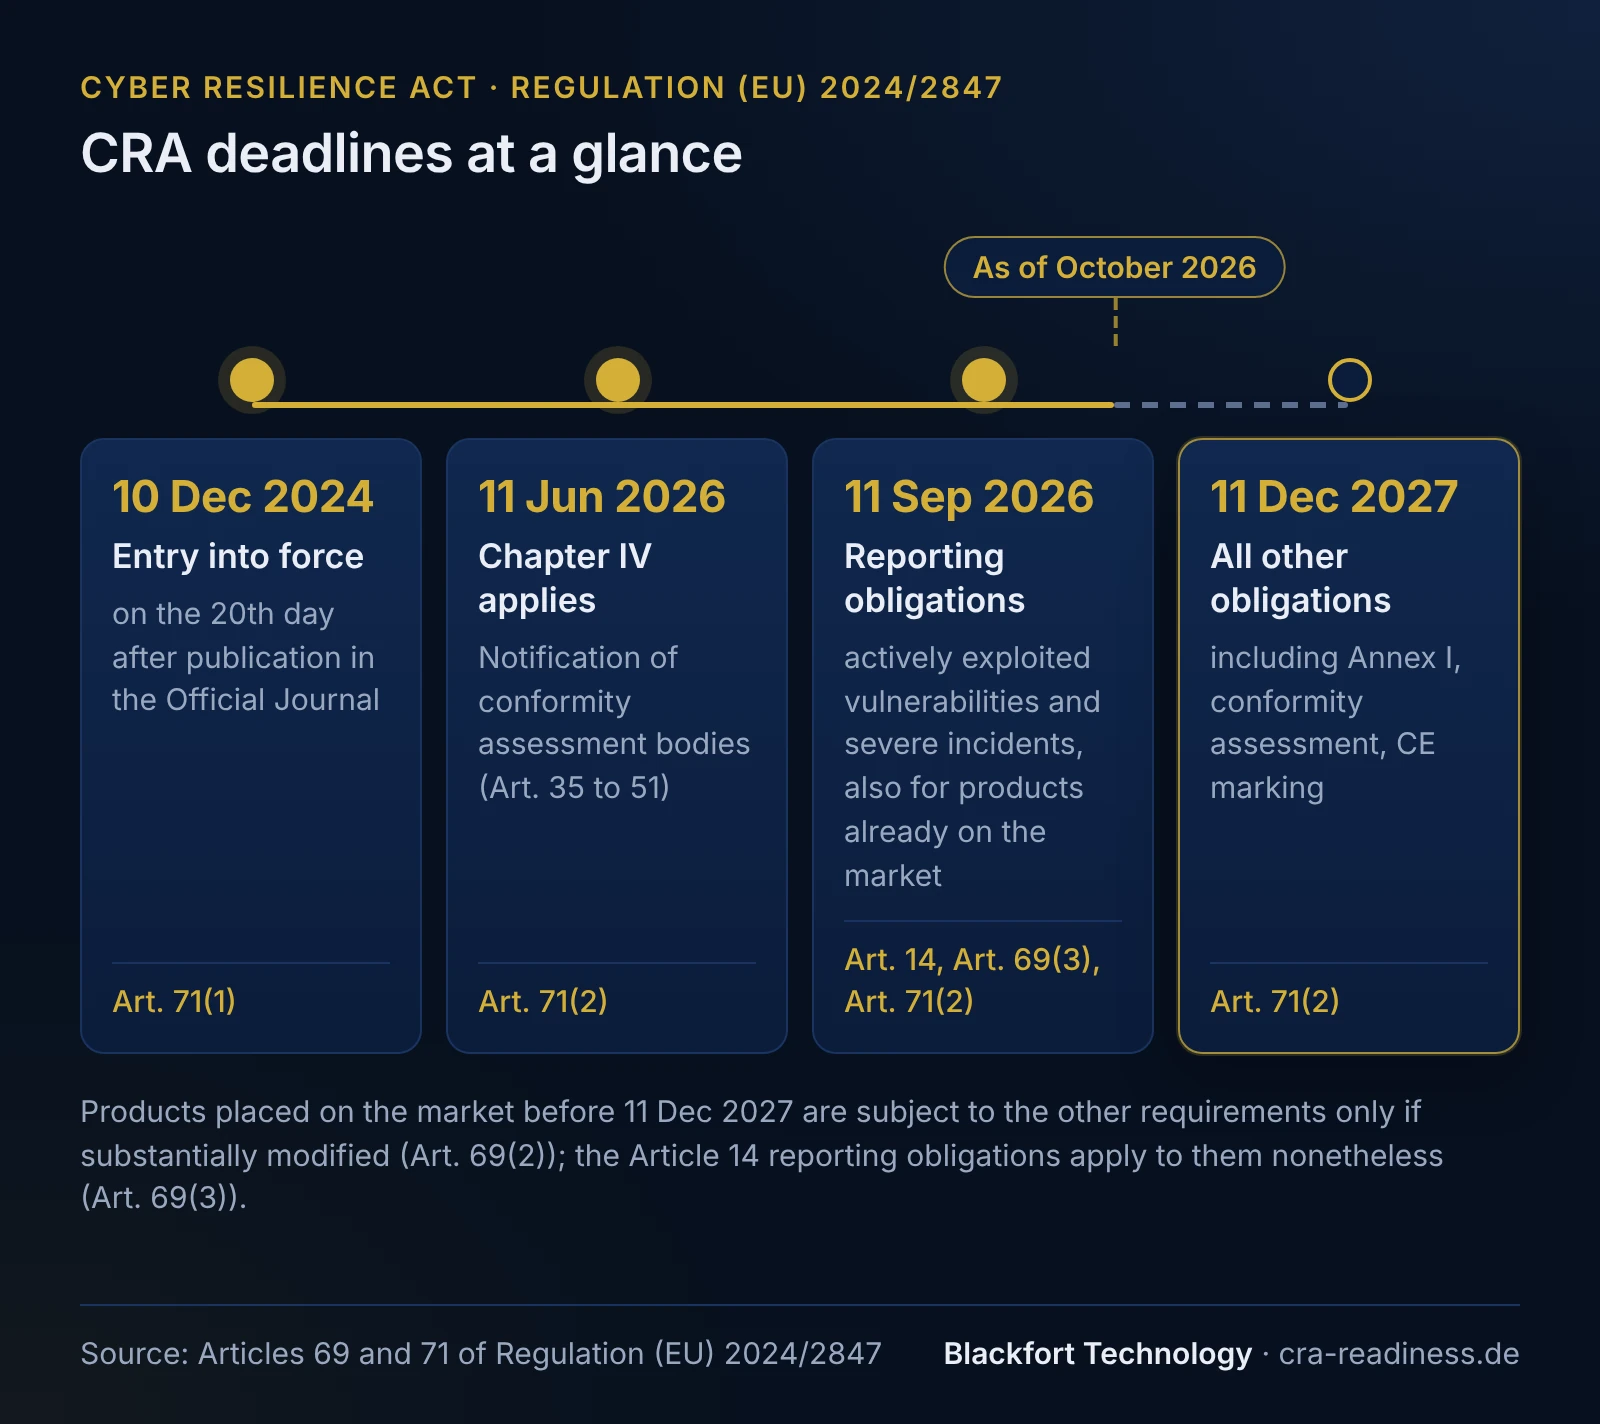
The CRA applies in stages. Three dates matter most in practice:
| Date | What applies from then on? |
|---|---|
| 11 June 2026 | Rules on notified bodies (Conformity Assessment Bodies) apply. |
| 11 September 2026 | Reporting and notification obligations for actively exploited vulnerabilities and severe incidents (Art. 14 CRA). This is the first hard operational deadline for manufacturers. |
| 11 December 2027 | Full applicability of all remaining product requirements: Security by Design, SBOM, CE marking, technical documentation, EU Declaration of Conformity. |
Without a working reporting process the Art. 14 CRA deadline is hard to meet when a reportable event occurs, even though the remaining product requirements only apply from December 2027. For details: CRA Notification Obligations since 11 September 2026: what applies now.
Who Is Affected by the CRA?
The CRA targets all economic operators along the supply chain who place products with digital elements on the EU market:
- Manufacturers: Anyone who develops or has developed a product and markets it under their own name or brand - including when offered free of charge.
- Importers: businesses established in the EU that place on the market a product bearing the name or trademark of a manufacturer established outside the EU.
- Distributors: Anyone who makes a product available on the EU market without being the manufacturer or importer - with graduated obligations.
A product with digital elements is a software or hardware product including its remote data processing solutions (Article 3(1)). It falls under the CRA if its intended purpose or reasonably foreseeable use includes a direct or indirect logical or physical data connection to a device or network (Article 2(1)). This includes mobile apps, industrial control systems, network devices, security software and many other categories.
No size exemption: SMEs and micro-enterprises are in principle in scope. Micro and small enterprises benefit from targeted relief, for example a simplified format for the technical documentation (Article 33(5)). Whether Article 64(10) exempts them from fines for a missed 24-hour early warning is, on its wording, a question of interpretation, because the provision only derogates from paragraphs 3 to 9; recital 120 points that way. The reporting obligation itself applies regardless of company size. There is no blanket exemption. More on this: CRA for SMEs.
Excluded are, among others, medical and in vitro diagnostic devices (MDR/IVDR), vehicles under Regulation (EU) 2019/2144, aviation products certified under Regulation (EU) 2018/1139 and marine equipment (Article 2(2) to (4)); further exclusions cover spare parts and national-security products (Article 2(6) and (7)). For all other products the connection criterion decides.
Still unsure whether your product is affected? Check your scope now - or read the in-depth article: Cyber Resilience Act - am I affected? Roles & exceptions explained.
Product Classes: What Applies to Which Product?
The CRA distinguishes default products, important products in classes I and II and critical products. The classification determines which conformity assessment procedure is required:
| Class | Typical products (examples) | Conformity assessment |
|---|---|---|
| Default | Memory chips, mobile apps, video games | Self-assessment (internal control, Module A) permissible |
| Important - Class I (Annex III) | Identity and access management software, browsers, password managers, VPN, SIEM, PKI, network management systems, malware detection, routers/modems/switches | Self-assessment (Module A) only with full application of harmonised standards, common specifications or a European cybersecurity certification scheme (at least “substantial”); otherwise third-party assessment by a notified body (Module B+C or H) |
| Important - Class II (Annex III) | Hypervisors, container runtimes, firewalls, IDS/IPS, tamper-resistant microprocessors/microcontrollers | Notified body (Module B+C or H) or, where available, a European cybersecurity certification scheme at assurance level at least “substantial” |
| Critical (Annex IV) | Smart cards, secure elements, smart meter gateways | Notified body mandatory in all cases, or mandatory EU cybersecurity certification scheme |
Technical descriptions for important and critical products are specified further in Implementing Regulation (EU) 2025/2392. Classifying a specific product may require interpretation in individual cases - blanket self-assessments are not appropriate here. More on classification: CRA product classes: classification & conformity pathways.
Notification Obligations since 11 September 2026
Since 11 September 2026, manufacturers have been required to report actively exploited vulnerabilities and severe incidents affecting the security of their products. The timelines are tight:
- 24 hours: early warning without undue delay and in any event within 24 hours of becoming aware
- 72 hours: notification without undue delay and in any event within 72 hours, with the general information available and the corrective or mitigating measures taken
- 14 days: Final report for vulnerabilities - no later than 14 days after a corrective measure becomes available
- 1 month: Final report for severe incidents - within one month of the 72-hour notification
Reports are submitted centrally via the single reporting platform (SRP) that ENISA sets up under Art. 16 CRA. The notification goes simultaneously to the CSIRT designated as coordinator, as a rule that of the member state of the manufacturer's main establishment, and to ENISA.
Meeting these deadlines requires prior preparation: an established PSIRT process, a maintained SBOM for rapid vulnerability identification, and clear internal escalation paths. Without this foundation the 24-hour deadline is hard to meet when a reportable event occurs.
Details and recommended actions: CRA notification obligations since 11 September 2026: 24h/72h/14-day timelines explained.
Core Obligations for Manufacturers
For products placed on the market from 11 December 2027, the full requirements of Art. 13 and Annex I and II apply; products placed on the market earlier are covered in this respect only if they are substantially modified (Art. 69(2)):
- Security by Design and Security by Default: Cybersecurity must be embedded from the outset in product design and development - as a default, not an option.
- Cybersecurity risk assessment: Systematic evaluation throughout the entire lifecycle (planning, design, development, production, delivery and maintenance).
- Vulnerability management over the support period: Coordinated vulnerability disclosure, patch provision, communication of end-of-support dates.
- Software bill of materials (SBOM): in a commonly used machine-readable format, covering at least the top-level dependencies, as part of the technical documentation and the basis for vulnerability handling.
- Technical documentation: To be kept available for market surveillance authorities.
- CE marking: After successful conformity assessment.
- EU Declaration of Conformity: Formal proof of compliance with CRA requirements.
- User information (Annex II): Transparent communication about security properties and support period.
SBOM requirements in detail - formats, archiving obligations, depth: SBOM requirements under the CRA: CycloneDX vs. SPDX, TR-03183-2 & archiving.
CRA Readiness: Where Do Your Processes Stand Today?
The first operational deadline (11 September 2026) has passed. CRA readiness means tackling the measures in the right order:
- Clarify scope and product class - What applies to which product?
- Establish notification processes - PSIRT, escalation paths, SRP connectivity - immediately, as the reporting obligation has applied since September 2026.
- Build SBOM foundations - Component inventory, dependency tracking, format selection (BSI TR-03183-2 requires CycloneDX 1.6 or higher / SPDX 3.0.1 or higher).
- Anchor Security by Design - Integrate risk assessments into development processes.
- Prepare conformity assessment - Technical documentation, and where applicable, engage a notified body.
Which steps make sense for your product and in which order depends on your starting point. A prioritised implementation plan for SMEs and mid-size companies: Cyber Resilience Act for SMEs: Prioritised implementation plan 2026/2027.
How Blackfort Technology Supports Your CRA Implementation
Blackfort Technology provides technical and organisational support to manufacturers, importers and distributors on the path to CRA Readiness. Blackfort Technology brings hands-on implementation experience from PKI projects, DORA and NIS2 mandates, ISMS build-outs, and vulnerability and patch management engagements. Blackfort Technology is represented in the AI security expert group of the Alliance for Cyber Security through its managing director, who is co-author of the guideline on penetration testing of large language models published there.
Key areas of support:
- Scope analysis and product classification: Technical assessment of the product class per product based on the CRA text and Implementing Regulation (EU) 2025/2392; we flag legal questions for review by your legal department.
- SBOM build-out and gap analysis: Component inventory, format selection, integration into existing development processes. For an initial assessment: Request an SBOM Gap Report (cra-sbom.de).
- Vulnerability management and PSIRT establishment: Process design and operational support for building a Product Security Incident Response Team capable of meeting the 24h/72h notification deadlines.
- Security by Design integration: Embedding cybersecurity risk assessments into existing development and quality assurance processes.
- Conformity assessment preparation: Technical documentation, self-assessment (Module A) or support when engaging a notified body.
For SMEs we prioritise the measures by deadline and risk, in plain language. Our SME offering at a glance.
Further Reading
- Cyber Resilience Act - am I affected? Roles & exceptions explained
- CRA notification obligations since 11 September 2026: 24h/72h timelines and PSIRT build-out
- SBOM requirements under the CRA: CycloneDX vs. SPDX, TR-03183-2 & archiving
- CRA product classes: Default, Class I/II and Critical - classification & conformity pathways
- Cyber Resilience Act for SMEs: Prioritised implementation plan 2026/2027
Frequently asked questions
When does the Cyber Resilience Act apply?+
As a software manufacturer, am I affected by the CRA?+
What is an SBOM and why does it matter for the CRA?+
What happens if I fail to meet the notification obligations that have applied since September 2026?+
Does the CRA apply to open-source software?+
Sources
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).