
Last updated: 2026-10-09
Before a product with digital elements (PDE) may be placed on the EU market under the Cyber Resilience Act (Regulation (EU) 2024/2847), the manufacturer must demonstrate that it meets the essential requirements of Annex I. This proof is provided through a conformity assessment under Article 32, followed by an EU declaration of conformity (Art. 28) and CE marking (Art. 30). It is a misconception that a notified body must always be involved. That is not the case: default-category products assess themselves, and Class I products can do so too under the conditions described below. Which route applies depends on the product class. The following is general technical and organisational information and does not replace legal advice in an individual case; the final classification of a specific product depends on its functions and its particular context of use.
Timeline: The CRA entered into force on 10 December 2024. The reporting obligations under Art. 14 have applied since 11 September 2026. General application - and with it the obligation to carry out conformity assessment and CE marking - begins on 11 December 2027. No CRA CE marking is mandatory before that date.
Four tiers, four routes
The CRA sorts products into four tiers. The classification determines whether self-assessment suffices or a third party must be involved. We cover the product classes separately under CRA product classes.
- Default / unclassified: all PDEs that are neither “important” (Annex III) nor “critical” (Annex IV). This is the general case.
- Important - Class I (Annex III, Class I): e.g. identity and privileged-access management, browsers, password managers, anti-malware, VPNs, network-management software, SIEM, operating systems, routers/modems/switches, general-purpose virtual assistants for the smart home or connected alarm systems.
- Important - Class II (Annex III, Class II): e.g. hypervisors and container runtimes, firewalls/IDS/IPS, and tamper-resistant microprocessors and microcontrollers.
- Critical (Annex IV): e.g. hardware security modules (HSMs), smart meter gateways and other devices for advanced security purposes, such as secure cryptoprocessing, and smart cards / secure elements.
To find out whether your product falls within scope at all, start with our applicability check.
The assessment modules (Annex VIII)
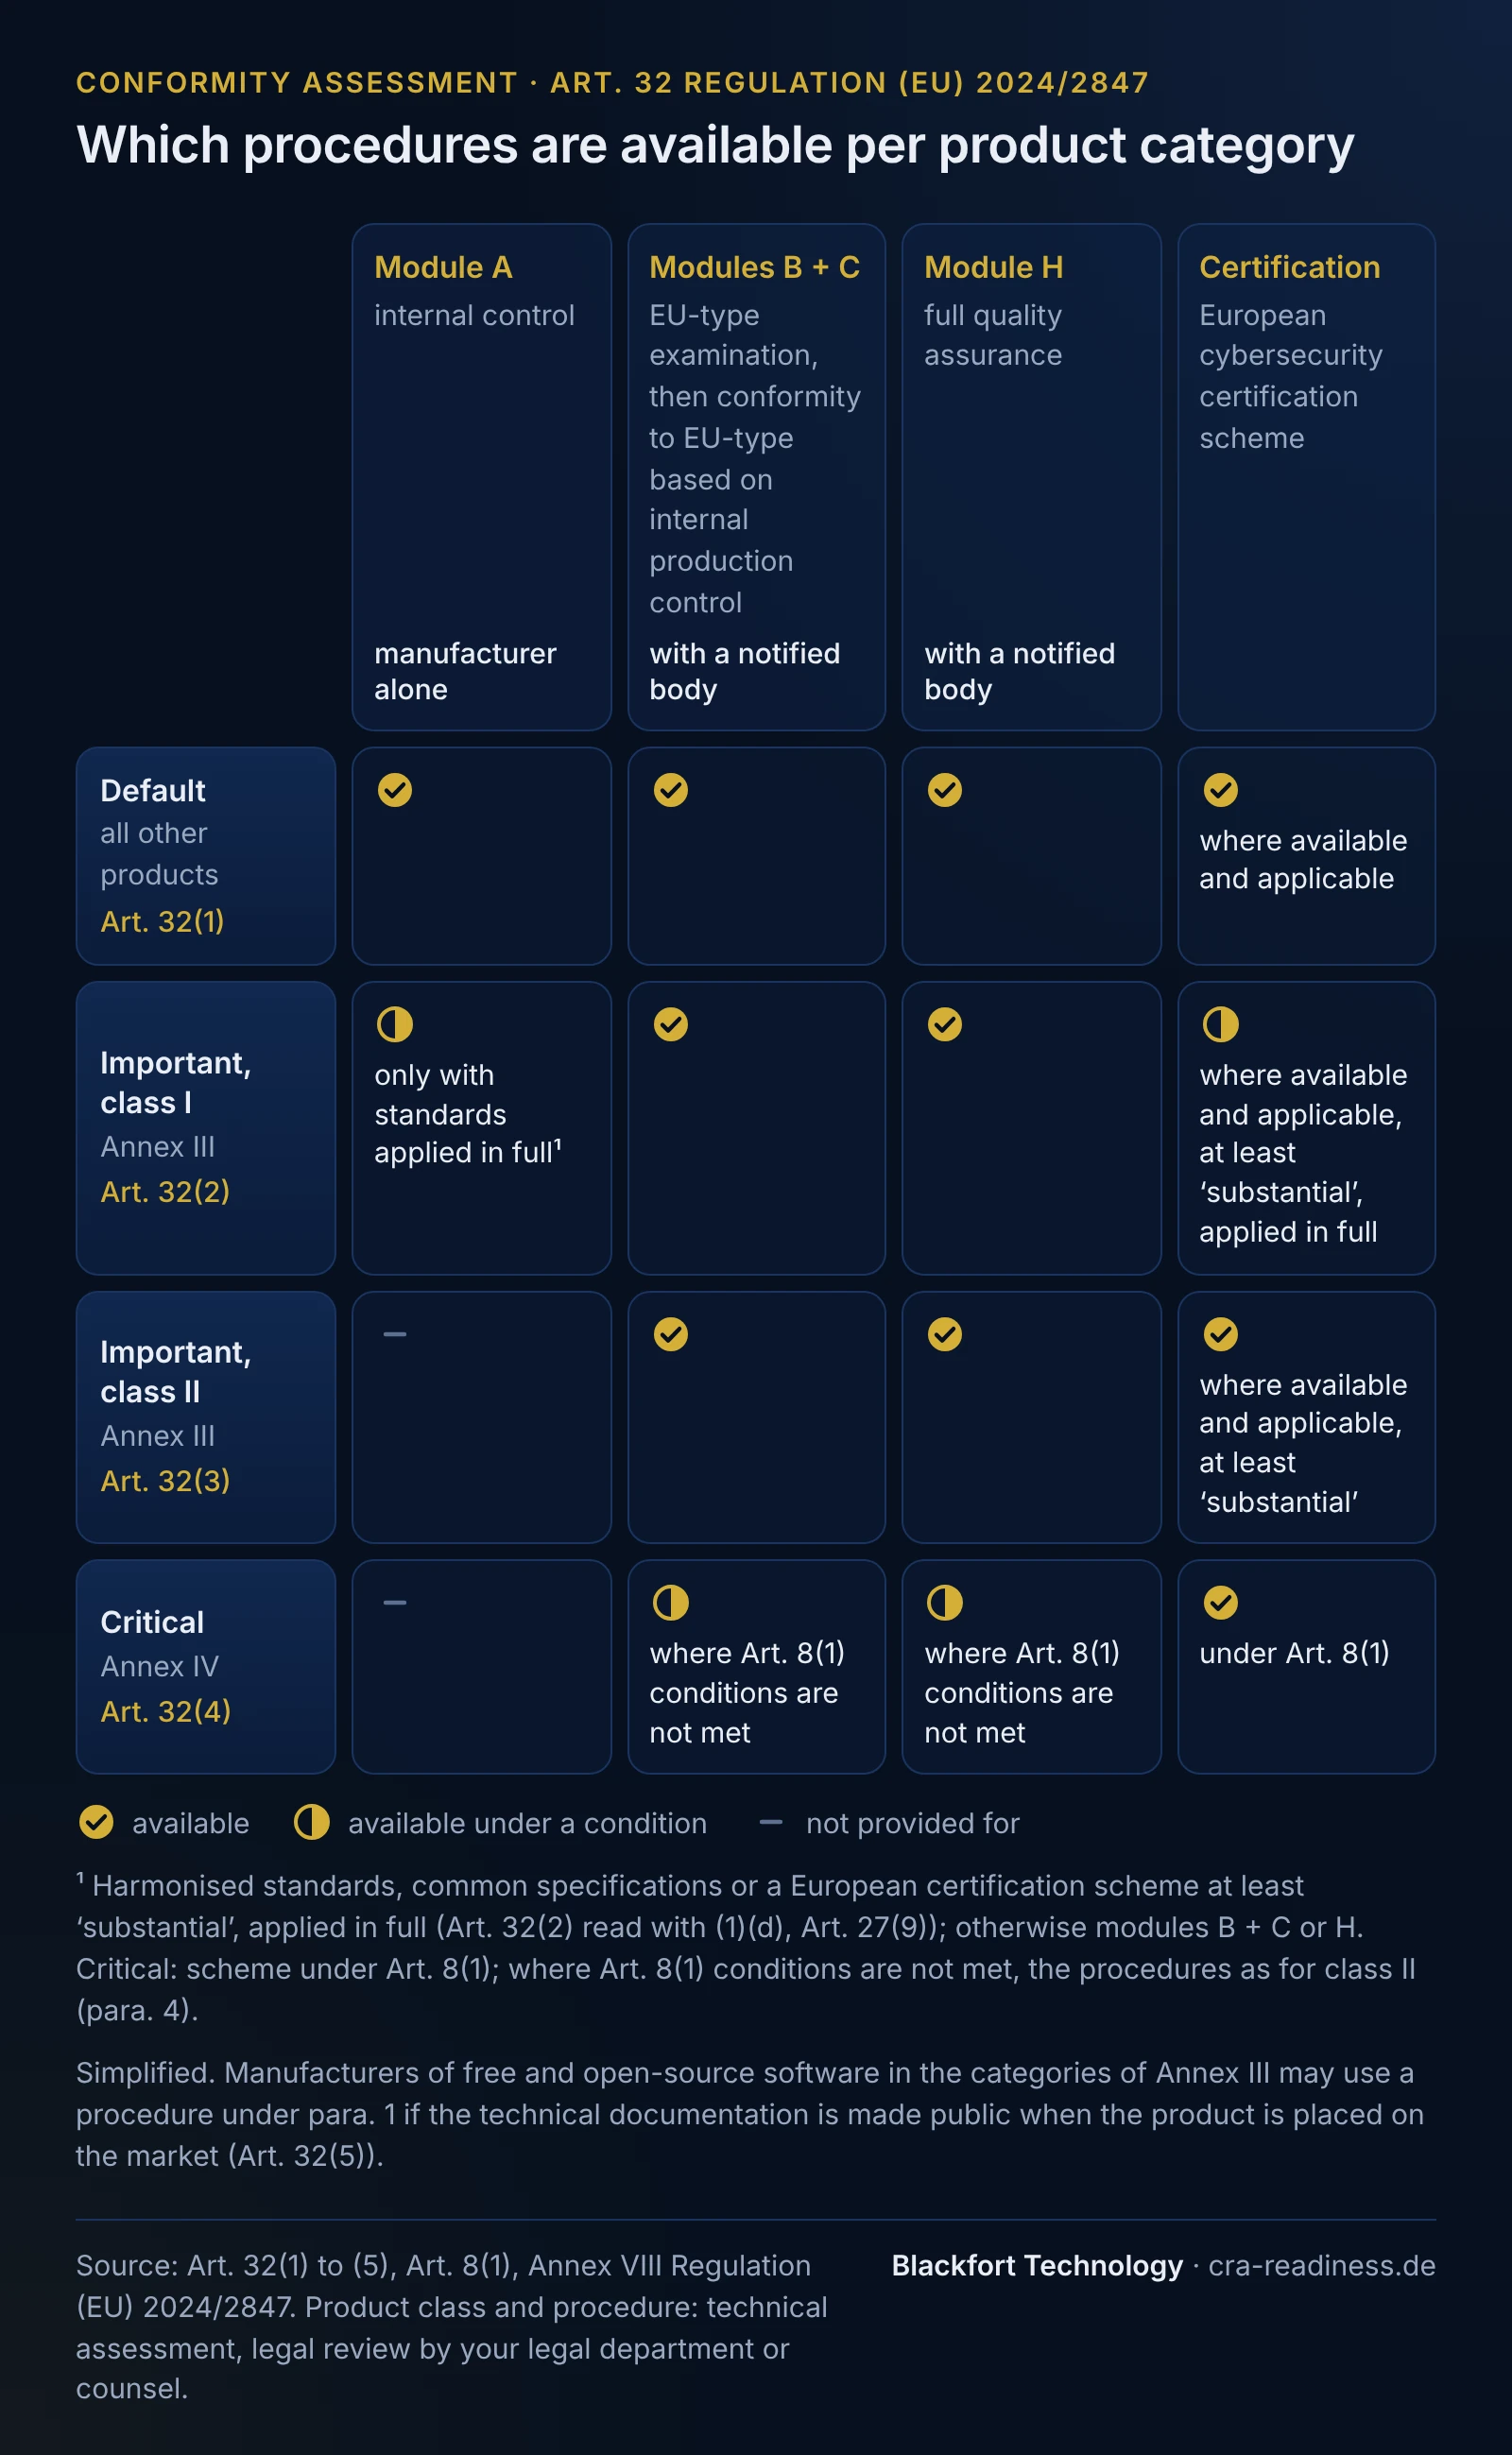
The specific assessment procedures - the “modules” - are set out in Annex VIII. Three routes are relevant in practice:
Module A - internal control (self-assessment)
The manufacturer verifies and declares, under its sole responsibility, that the product meets the requirements of Annex I, draws up the technical documentation (Annex VII), and then affixes the CE marking. No third party is involved. This is the default route for unclassified products (Art. 32(1)).
Module B + C - EU-type examination plus conformity to type
A notified body examines the type (Module B, EU-type examination) and issues a certificate; the manufacturer then uses internal production control to ensure that production conforms to the examined type (Module C).
Module H - full quality assurance
A notified body assesses and monitors the manufacturer’s quality-management system across the full lifecycle (design, development, production). Module H suits manufacturers who maintain a broad product range and want to apply one assessed system to several products rather than having each type examined individually.
In addition to these modules, a European cybersecurity certification scheme under Regulation (EU) 2019/881 can, where available and applicable, serve as a route of proof across all tiers (Art. 32(1)(d), (3)(c), (4)); for important and critical products at assurance level at least “substantial”. The category descriptions of important and critical products are further specified by Commission Implementing Regulation (EU) 2025/2392.
Which route for which tier?
| Tier | Permitted route (Art. 32) | Third-party assessment required? |
|---|---|---|
| Default / unclassified | Module A (self-assessment); alternatively B+C, H or a certification scheme | No - self-assessment (Module A) suffices |
| Important - Class I | Module A only if harmonised standards, common specifications or a European cybersecurity certification scheme (assurance level at least “substantial”) are fully applied; otherwise Module B+C or H | No if fully applied, otherwise Yes (notified body) |
| Important - Class II | Always via a third party: Module B+C or Module H with a notified body or, where available, a European cybersecurity certificate at least at assurance level “substantial” (Art. 32(3)) | Yes - no self-assessment |
| Critical | European cybersecurity certificate (Regulation (EU) 2019/881, at least “substantial”) where mandated by a delegated act under Art. 8(1); otherwise the Class II routes (Art. 32(4)) | Yes - no self-assessment |
Key point: Third-party assessment is mandatory in every case only for important Class II products and for critical products: Module B+C or H with a notified body, or a European cybersecurity certificate at least at assurance level “substantial”. Class I products may self-assess under Module A provided harmonised standards, common specifications or a European cybersecurity certification scheme (assurance level at least “substantial”) are fully applied; otherwise Module B+C or H applies. Default-category products self-assess anyway. So the claim “every product needs a notified body” is wrong.
Critical products and the certification scheme
For critical products under Annex IV, the Commission may require conformity to be demonstrated through a European cybersecurity certification scheme under Regulation (EU) 2019/881 (Cybersecurity Act) at an assurance level of at least “substantial” (Art. 8(1)). Where such a scheme is not (yet) mandated, the Class II routes are available (Art. 32(4)).
CE marking and the accompanying documents
Three documents or steps belong to the conformity assessment: the technical documentation, which is drawn up before placing on the market and forms the basis of the assessment (Art. 31(2)), followed by the EU declaration of conformity and the CE marking:
- Technical documentation (Annex VII): product description; design, development and production processes; vulnerability-handling processes (architecture, SBOM, CVD policy, update distribution); the risk assessment mapped to Annex I; support-period information; standards applied and test reports. It must be retained for at least ten years after placing on the market or for the duration of the support period, whichever is longer (Art. 13(13)).
- EU declaration of conformity (Art. 28, contents in Annex V): product identifier; details of the manufacturer or representative; declaration under sole responsibility; standards/specifications/schemes applied and - where applicable - the name, number and procedure of the notified body.
- CE marking (Art. 30): by affixing the CE mark, the manufacturer declares conformity with the requirements of the CRA.
Consequences of a missing or incorrect assessment
The conformity obligations carry the risk of fines. Breaches of the essential requirements in Annex I and of core manufacturer duties can be penalised with fines of up to EUR 15 million or 2.5% of total worldwide annual turnover (whichever is higher). For further obligations - including parts of the conformity assessment, the declaration of conformity and CE marking - the range is up to EUR 10 million or 2%. Incomplete or misleading information to notified bodies or market-surveillance authorities can be penalised with up to EUR 5 million or 1%. These ranges are lower than under the GDPR - the top tier is EUR 15 million or 2.5%.
What manufacturers should do now
Even though the CE obligation only takes effect from 11 December 2027, an early start pays off: standards mapping, risk assessment, technical documentation and - for Class II or critical products - the early scheduling of a notified body all take time. Note that the harmonised standards and common specifications that, alongside a European certification scheme (at least “substantial”), first open the self-assessment route for Class I are still partly under development; their full application presupposes that they are available in time. It makes sense to first determine the product class, then choose the appropriate assessment route, and build the documentation continuously - ideally so that it is ready for inspection by the deadline. Our page on the Cyber Resilience Act gives an overview of the whole legal act.
Frequently asked questions
Does every product under the CRA need a notified body?+
What do Modules A, B+C and H mean?+
From when is CE marking mandatory under the CRA?+
Which documents belong to CE marking?+
How are critical products assessed?+
Sources
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).