
Last updated: 2026-10-09
What Blackfort Technology Does for You
You commission the modules you need. The recommended first engagement is the gap analysis at a fixed price for the scope we agree in the free initial call; you then decide, with facts on the table, how far the programme should go.
- CRA gap analysis: product register, roles, product classes and a gap report per product with a prioritised action plan.
- Threat modeling and risk assessment: the risk assessment under Article 13(2) to (4), kept as a threat model in code and re-run on a changed release.
- SBOM and vulnerability management: a software bill of materials per release from the build pipeline and one chain for vulnerability findings. For a quick review of an existing SBOM: SBOM gap report.
- Reporting process and PSIRT: roles, runbook and decision aid for the Article 14 reporting obligation, which has applied since 11 September 2026.
- Technical documentation and conformity: Annex VII, user information and preparation of the conformity assessment up to the EU declaration of conformity.
- External product security officer: a named point of contact who coordinates the backlog, customer requests and evidence on an ongoing basis.
- CRA readiness audit for management: if your CRA programme is already running, we review it independently of the project lead based on samples and rate where each product stands.
- Also available: CRA and IEC 62443, EN 18031 for radio equipment, CRA workshop and CRA funding for SMEs.
Since 11 September 2026: The Cyber Resilience Act Reporting Obligations Apply
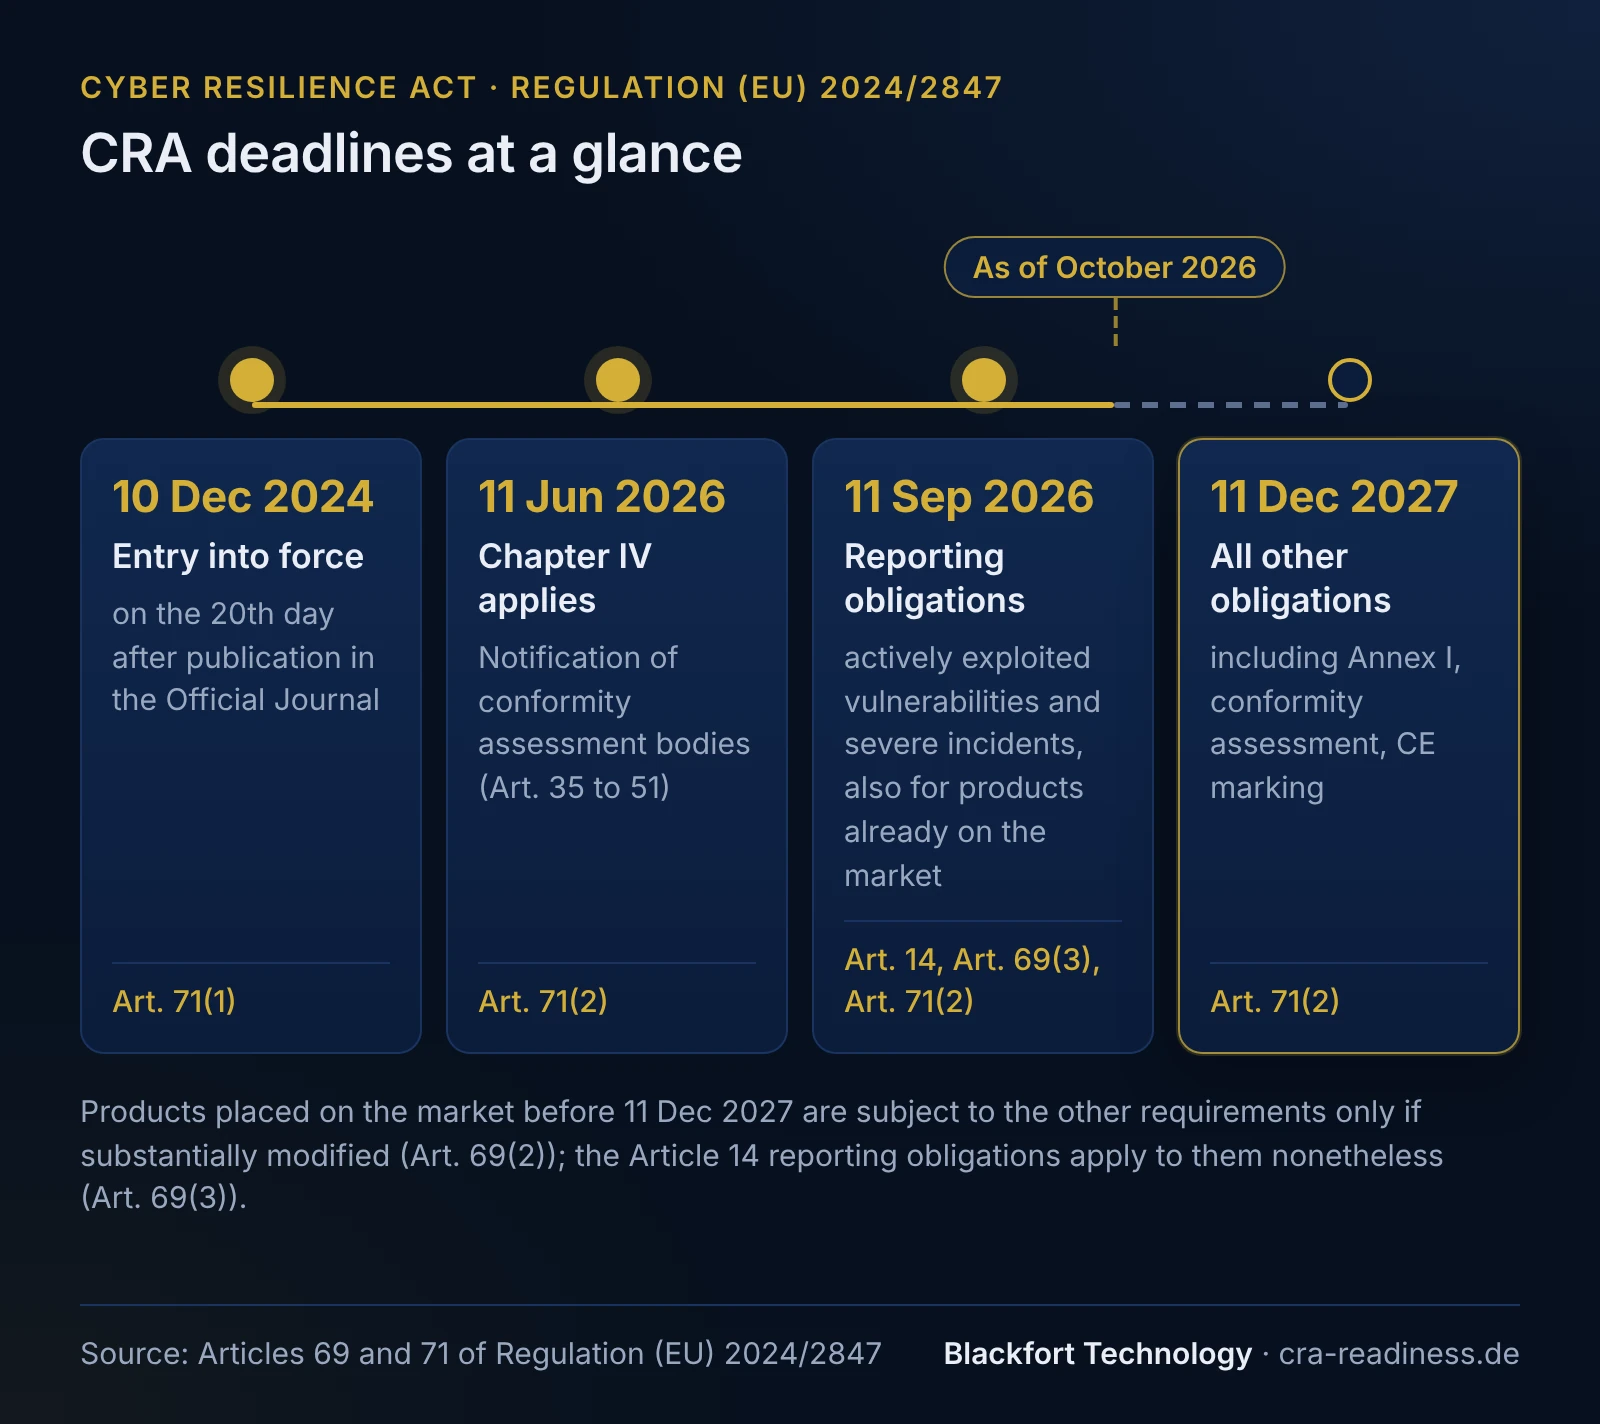
Since 11 September 2026, manufacturers of products with digital elements have been subject to binding reporting obligations under Regulation (EU) 2024/2847, the Cyber Resilience Act (CRA). Actively exploited vulnerabilities and severe incidents must be reported via the single reporting platform simultaneously to the CSIRT designated as coordinator and to ENISA: early warning without undue delay and in any event within 24 hours, notification within 72 hours, final report 14 days after a corrective measure is available (vulnerabilities) or one month after the notification (incidents).
The remaining manufacturer obligations apply from 11 December 2027. Harmonised standards will make demonstrating conformity easier later; the reporting process, product register and SBOM can be built today without them.
Am I in scope? Find out now.
The CRA applies to manufacturers, importers and distributors of products with digital elements made available on the EU market in the course of a commercial activity, whether for payment or free of charge (Article 3(22)). Check the scope early, including for software, accessories and components.
Use the interactive scope check to get an initial assessment in minutes: What role do you play (manufacturer, importer, distributor)? Does your product fall under the CRA? And if so, what product class is it likely to fall into?
SMEs: No Size Exemption, but Clear Priorities
The Cyber Resilience Act does not provide a general exemption for SMEs. Smaller manufacturers of products with digital elements are in scope. There are, however, targeted relief provisions for micro and small enterprises, for example a simplified format for the technical documentation (Article 33(5)). Whether Article 64(10) exempts them from fines for a missed 24-hour early warning is, on its wording, a question of interpretation, because the provision only derogates from paragraphs 3 to 9; recital 120 points that way.
What matters most for SMEs: what to tackle first. Reporting processes (mandatory since September 2026) take priority over SBOM completeness and CE marking (deadline: December 2027). Knowing the priorities avoids unnecessary effort.
Knowledge: Background and Technical Detail
- CRA reporting obligations since 11 September 2026: 24h/72h explained
- Am I affected by the Cyber Resilience Act? Roles and exceptions
- CRA product classes: default, class I/II and critical
- SBOM requirements under the CRA: CycloneDX, SPDX, TR-03183-2
- Cyber Resilience Act for SMEs: a prioritised implementation plan
Frequently asked questions
When does the Cyber Resilience Act apply?+
As a software manufacturer, does the CRA apply to me?+
What do I need to have in place as a manufacturer for the reporting obligation?+
Does the CRA also apply to SMEs and small software companies?+
What is an SBOM and why is it relevant for the CRA?+
Sources
- Regulation (EU) 2024/2847 (Cyber Resilience Act) - EUR-Lex
- Implementing Regulation (EU) 2025/2392 (category descriptions Annex III/IV)
- European Commission - Cyber Resilience Act (policy page)
- European Commission - Cyber Resilience Act summary
- European Commission - CRA reporting obligations
- European Commission - CRA conformity assessment
- ENISA - Single Reporting Platform (SRP)
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).