
CRA readiness audit
CRA readiness audit: where does your CRA programme really stand?
Your organisation reports progress on the Cyber Resilience Act. We check how much of it is evidenced. Whether your own team or a service provider is implementing it, Blackfort Technology reviews the CRA programme independently of the project lead, looking at scope, evidence and reporting capability, with samples taken from code, processes and documents. You receive a report you can read without specialist knowledge, with a rating per product and the points that need a management decision.
Why an independent review
As the manufacturer, your company is responsible for the CRA manufacturer obligations. The Article 14 reporting obligation has applied since 11 September 2026; the other manufacturer obligations apply from 11 December 2027 (Article 71(2)). Upon a reasoned request from the market surveillance authority, the manufacturer must provide all information and documentation needed to demonstrate the conformity of the product and its processes with Annex I (Article 13(22)). For non-compliance with the essential cybersecurity requirements in Annex I and the obligations in Articles 13 and 14, Article 64(2) provides for fines of up to EUR 15 million or, for undertakings, up to 2.5% of total worldwide annual turnover for the preceding financial year, whichever is higher.
A status report from your own project tells you what has been done. The review shows you, based on samples, where the programme stands: whether all products are covered, whether the evidence exists and can be followed when the market surveillance authority asks for it, and whether the reporting chain is staffed at night and at weekends. To answer that, we look at the evidence ourselves.
What management receives
A report you can read without specialist knowledge, with ratings your team can trace back to the evidence.
01
Result on one page
Overall picture with a rating per product and review area, the main risks and the decisions that rest with you.
02
Findings with evidence
For each rating the sample reviewed, so that project lead and development can follow it.
03
Recommendations by urgency
What is needed now, for example for the reporting obligation that already applies, and what must be done by 11 December 2027.
04
Project lead response
With your consent, the project lead sees the findings in advance. If their response arrives within the agreed period, it is included in the report.
05
Closing meeting
Walk-through with management, together with the project lead if you wish.
Management summary: what the result looks like
Extract from the overview of a review report, a fictitious example with two products. Overall status: action needed, evidence partly reliable.
| Review area | Controller A | Gateway B | Main finding |
|---|---|---|---|
| Scope and product register | partly evidenced | evidenced | Two older variants of controller A are missing from the register. |
| Risk assessment and Annex I | partly evidenced | not evidenced | No documented risk assessment exists for gateway B. |
| Vulnerabilities and SBOM | evidenced | partly evidenced | Gateway B: an SBOM is produced, findings are not tracked. |
| Article 14 reporting capability | not evidenced | not evidenced | No deputy named outside business hours. |
| Documentation and governance | partly evidenced | partly evidenced | Support period not determined. |
Recommendation to management in the example: secure the reporting procedure with deputies at short notice, evidence the risk assessment for gateway B, determine the support period. Fictitious example for illustration, no customer data. "Evidenced" means the sample reviewed was complete and traceable. It is not a statement of conformity.
What we review
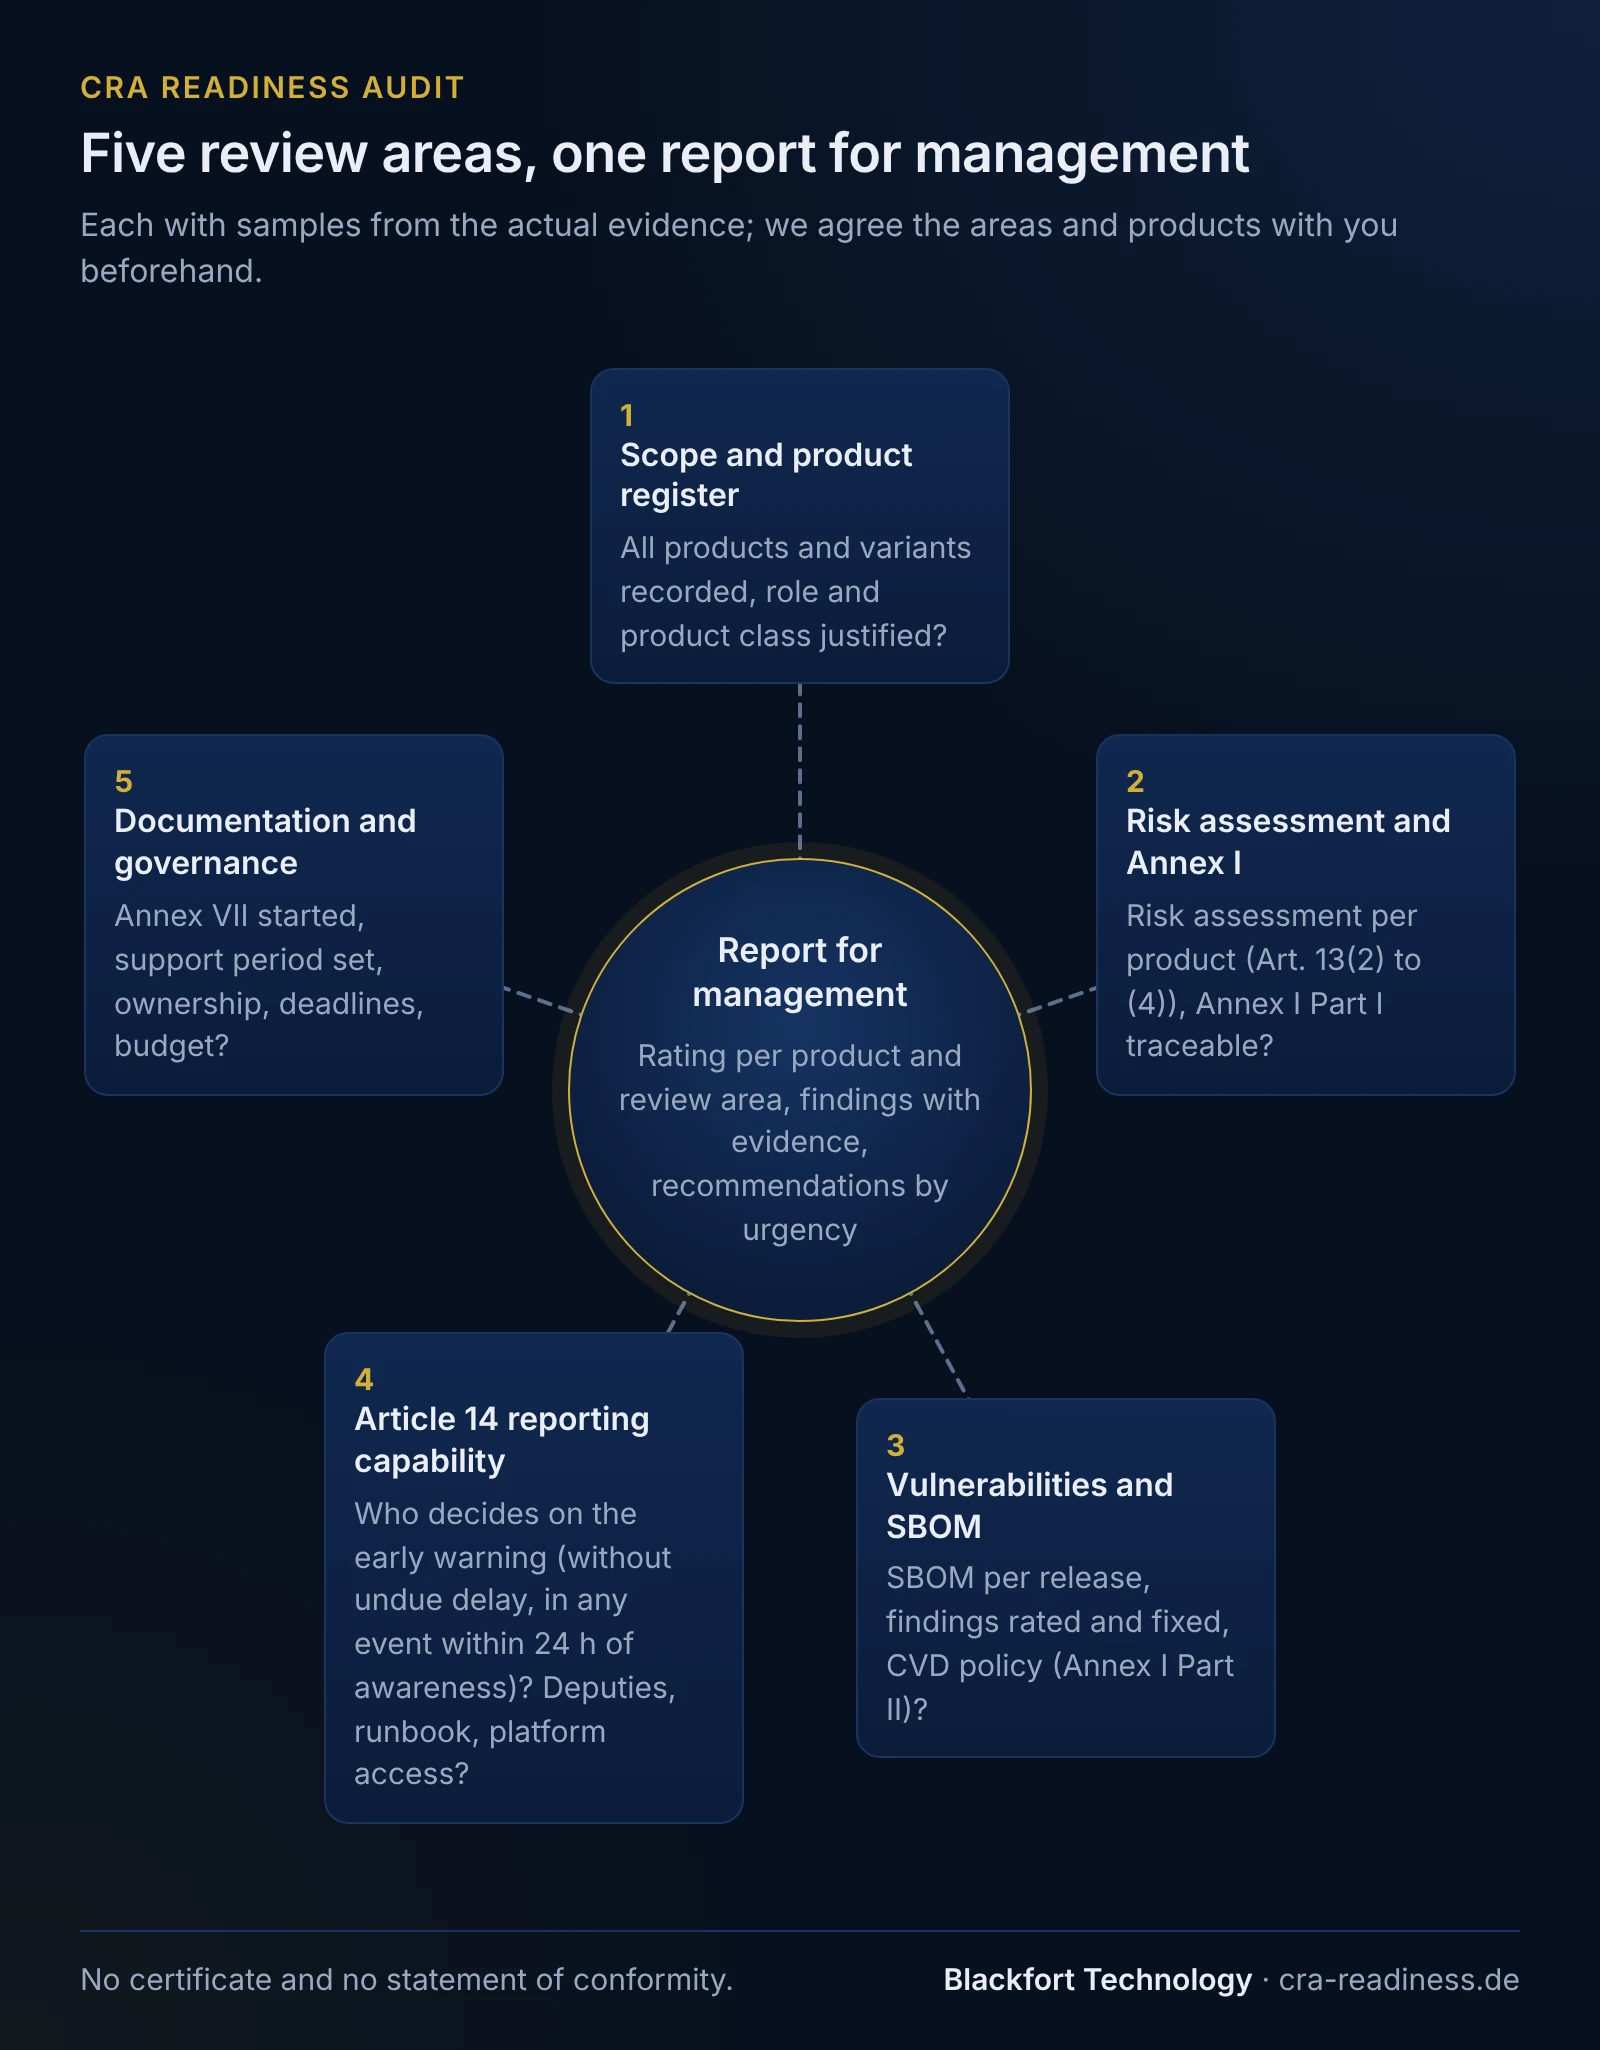
Five review areas, each with samples taken from the actual evidence. We agree with you beforehand which areas and products are covered.
Scope and product register
Are all products and variants with digital elements recorded, is it documented for each which role and product class your company assumes and why, and are open legal questions flagged for your legal department or counsel?
Risk assessment and Annex I
Is there a documented risk assessment per product under Article 13(2) to (4), and can the Annex I Part I requirements be traced to code, configuration and tests?
Vulnerabilities and SBOM
Is a software bill of materials produced per release, are vulnerabilities rated and remediated, and is there a coordinated vulnerability disclosure policy under Annex I Part II?
Article 14 reporting capability
Who decides on the early warning, which is due without undue delay and at the latest 24 hours after becoming aware? Are there deputies, a runbook and access to the single reporting platform?
Documentation and governance
Has the Annex VII technical documentation been started and the support period determined? Does the programme have ownership, deadlines and a budget that matches the open points?
CRA gap analysis or CRA readiness audit?
Two services for two starting points. The gap analysis starts implementation, the audit assesses one that is running.
| CRA gap analysis | CRA readiness audit | |
|---|---|---|
| Commissioned by | business unit, product management, development | management |
| Prerequisite | no CRA programme yet | CRA programme already running |
| Aim | identify gaps and plan measures | assess the status independently |
| Approach | together with your teams | samples from the evidence, independent of the project lead |
| Result | gap report per product and prioritised action plan | report for management with a rating per product |
| Next question | What do we need to implement? | Where do we need to step in? |
More on the gap analysis: https://cra-readiness.de/en/cra-gap-analysis
How the review runs
Five steps from the engagement to the closing meeting.
1
Engagement and scope
Initial call with management: products, review areas, contacts and dates. You then receive a proposal with a clearly defined scope.
2
Documents
Your team provides the existing evidence and read access to code, build and ticket system, on your infrastructure if you prefer.
3
Samples and interviews
We check the evidence ourselves and hold targeted interviews with project lead, development and operations.
4
Report
Rating per product and review area, findings with evidence, recommendations by urgency and, if you wish, the project lead's response.
5
Closing meeting
Joint walk-through with management. You then decide what comes next.
Your contact
Christian Gebhardt · Founder and managing director, Blackfort Technology
Christian Gebhardt, founder and managing director of Blackfort Technology, is happy to take your enquiry personally. In a free initial call you work out together what you need; the consulting is carried out by the Blackfort Technology team.
What "independent" means here
If Blackfort Technology has contributed to the CRA programme in your company, we disclose this before the engagement; you decide whether we carry out the review. Parts we implemented ourselves are marked in the report as not independently assessed. Blackfort Technology also advises on implementation. Implementing the recommendations is not part of the review; whether and by whom you have them implemented is your decision.
We report to the management that engages us.
Five questions the report answers
What is actually evidenced? Comparison of reported project status, processes in practice and verifiable evidence in the samples.
Where are our critical gaps? Assessment of the main risks, starting with the reporting obligation that already applies.
Do planning and ownership match the open points? Assessment of planning, ownership and implementation status.
Which decisions rest with me? Recommendations by urgency, naming who has to decide.
How do I track progress? Milestones and evidence you can ask your team for in future.
What we do not do
So that expectations are right from the start:
- We do not provide legal services. Questions that have to be decided legally, such as scope, role or product class, are flagged for your legal department or counsel.
- We are not a notified body. The report is neither a certificate nor an attestation and does not replace the conformity assessment under Article 32.
- The review is based on samples. It shows the state of the evidence reviewed and does not establish that all requirements are met.
- We are not an audit firm. The report contains no audit opinion and no attestation.
- Penetration testing is not part of our offering.
The CRA obligations remain with your company. We help you meet them and demonstrate that you do.
Frequently asked questions
Who is the review for?+
For the management of manufacturers whose CRA programme is already running, in-house or with a service provider, and who want an independent assessment before releasing budget or answering customers.
Is this a CRA audit, a compliance check or a certification?+
The Regulation does not define a "CRA audit". It refers to audits in the conformity assessment carried out by notified bodies (Annex VIII). Our review is an assessment of where you stand, based on samples, with no certificate and no attestation. The conformity assessment under Article 32 remains a separate step, involving a notified body depending on the product class. A free online self-check is available at https://cra-readiness.de/en/affected.
Can you review work done by another service provider?+
Yes. We assess the results against the evidence and make no statements about how the provider works. With your consent, the project lead can respond to the findings. The report goes to the management that engages us.
What does the review cost?+
It depends on the number of products and review areas. After a free initial call you receive a proposal with a clearly defined scope.
How much work is it for our team?+
Your team provides the existing documents and access and is available for targeted interviews. We agree the scope beforehand so that your team can plan the effort.
Further reading
- CRA gap analysis
- CRA consulting and implementation
- Reporting process and PSIRT
- The CRA for management
- Who is liable for CRA infringements?
- What evidence management should ask for
- CRA audit: process, scope and cost
- Manufacturer obligations
- Fines and penalties
- Timeline and deadlines
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).
Last updated: 2026-10-09
Kontakt aufnehmen
Request a review
Tell us about your products and where your CRA programme stands. The initial call is free and without obligation; we usually reply within one to two working days.