
CRA consulting
CRA consulting: implementing the Cyber Resilience Act in your company
Blackfort Technology helps manufacturers of products with digital elements, such as connected devices, embedded systems and software, implement the Cyber Resilience Act: from the initial assessment and gap analysis to a working process and security evidence an assessor can follow in the technical documentation.
Where manufacturers stand today
The Article 14 reporting obligations have applied since 11 September 2026: actively exploited vulnerabilities and severe incidents having an impact on the security of the product must be reported, with an early warning without undue delay and in any event within 24 hours of the manufacturer becoming aware of them. This includes products that are already on the market. From 11 December 2027 all remaining manufacturer obligations apply, from the essential requirements in Annex I to the technical documentation and CE marking.
You may already have some of this in place: an ISMS, security reviews in development, a vulnerability tool. The CRA additionally requires the link to the individual product and evidence that an assessor or customer can follow. That is where our consulting starts.
Services at a glance
You commission the modules you need. We recommend starting with the gap analysis; you then decide, with facts on the table, how far the programme should go.
Where do we actually stand?
Initial assessment and gap analysis
Product register, roles, product classes and a gap report per product against Annex I and the other obligations, with a prioritised action plan.
CRA gap analysisWhere does our CRA programme really stand?
CRA readiness audit for management
We review a running CRA programme independently of the project lead, with samples from the evidence, and report to management with a rating per product and recommendations by urgency.
CRA readiness auditIs our product in scope?
Scope, roles and product classes
The technical basis for deciding which products fall under the CRA: product inventory, supply relationships, functions and intended use, compared with Annex III and IV. From that, a technical assessment of role, product class and possible conformity assessment route for review by your legal department or counsel.
Free scope checkHow do we evidence the risk assessment?
Cybersecurity risk assessment per product
The risk assessment under Article 13(2) to (4), documented for the technical documentation. We derive architecture, data flows and trust boundaries from source code and deployment configuration and keep the threat model as code in your repository, so it can be re-run on a changed release.
Threat modeling and risk assessmentWhat is in our release?
SBOM and vulnerability management
A machine-readable software bill of materials per release from the build pipeline, one consolidated chain for vulnerability findings and clear rules for rating and remediation under Annex I Part II.
SBOM consultingWho reports within 24 hours?
Article 14 reporting and CVD
The path from an incoming report to a decision, a decision aid for "actively exploited?", roles with deputies, a runbook for early warning, notification and final report, and a coordinated vulnerability disclosure policy with security.txt.
Reporting process and PSIRTWhat goes into the technical documentation?
Technical documentation and conformity
Building and reviewing the technical documentation under Annex VII, user information under Annex II, the support period and preparing the conformity assessment up to the EU declaration of conformity.
Documentation and conformityWe already work to IEC 62443
CRA and IEC 62443-4-1
We map Annex I to the practices of your secure development lifecycle and assess only what the CRA still needs.
CRA and IEC 62443Nobody holds the CRA threads together
External product security officer
A named point of contact from our team steers the backlog, customer requests and evidence, in three tiers and beyond the conformity assessment.
Product security officerThe team needs a shared understanding
CRA workshop
Your team works through the Cyber Resilience Act using its own products, on site or by video conference.
CRA workshopOur product has a radio interface
EN 18031 and the Radio Equipment Directive
Scope under Article 3(3)(d), (e) and (f), gap analysis against EN 18031 and documentation, linked to the CRA.
EN 18031Can this be funded?
CRA funding for SMEs
The second SECURE Open Call co-finances 50% up to EUR 30,000, deadline 11 December 2026. We can carry out the gap analysis as an external service provider in your project; you submit the application.
CRA fundingWhat you end up with
Every module ends with a result you can use internally, with customers or in an assessment.
01
CRA product register
Technical assessment: which products, which role, in scope or not, with the facts it is based on.
02
Gap report and action plan
Rated findings per product, actions with effort and date, ordered by urgency.
03
Threat model as code
Risk assessment documented for Annex VII, the model re-runnable on a changed release.
04
Reporting readiness
Named roles, runbook and decision aid for the Article 14 deadlines.
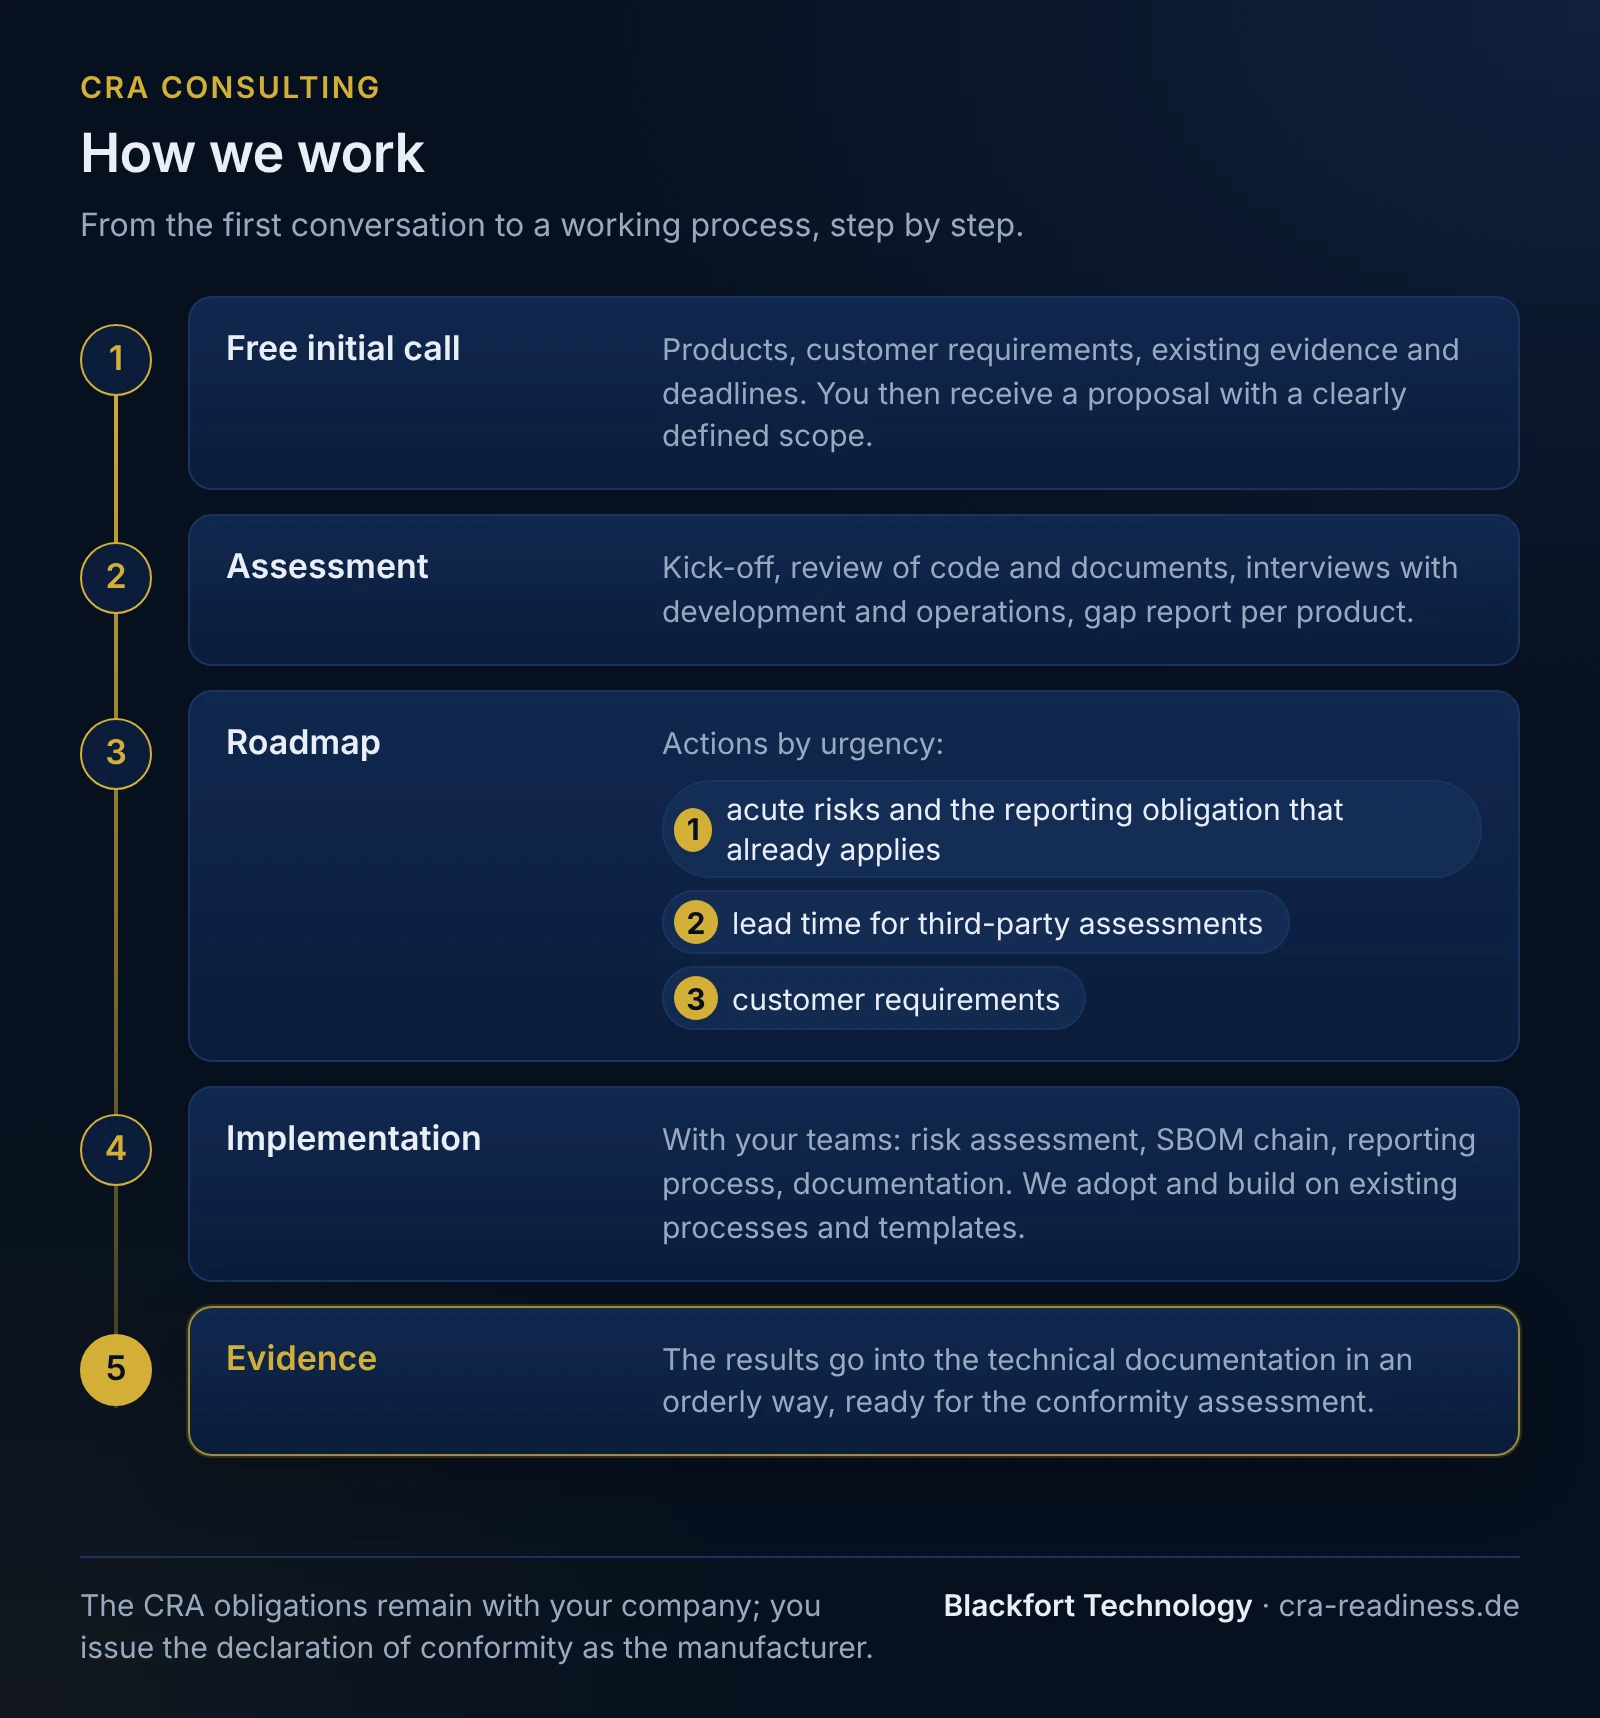
How we work
From the first conversation to a working process, step by step.
1
Free initial call
Products, customer requirements, existing evidence and deadlines. You then receive a proposal with a clearly defined scope.
2
Assessment
Kick-off, review of code and documents, interviews with development and operations, gap report per product.
3
Roadmap
Actions by urgency: acute risks and the reporting obligation that already applies first, then lead time for third-party assessments, then customer requirements.
4
Implementation
We build what is missing together with your teams: risk assessment, SBOM chain, reporting process, documentation. Existing processes and templates are adopted rather than duplicated.
5
Evidence
The results go into the technical documentation in an orderly way, ready for the conformity assessment.
Your contact
Christian Gebhardt · Founder and managing director, Blackfort Technology
Christian Gebhardt, founder and managing director of Blackfort Technology, is happy to take your enquiry personally. In a free initial call you work out together what you need; the consulting is carried out by the Blackfort Technology team.
What does CRA consulting cost?
We do not quote a flat fee, because the effort depends on three things: the number of products and variants, the product class (third-party assessment needs more documentation and lead time), and how much evidence already exists, for example from an ISMS, a development process certified to IEC 62443-4-1 or your customers' requirements.
That is why we start with a free initial call and then prepare a proposal with a clearly defined scope. We recommend the gap analysis as the first engagement: afterwards the remaining effort per product can be planned reliably, and you only commission the modules that are actually missing.
CRA consulting for SMEs
The CRA applies regardless of company size. Relief exists only in specific points, for example: micro and small enterprises may provide the technical documentation in a simplified format that the Commission lays down by implementing acts (Art. 33(5)).
For mid-sized manufacturers without their own regulatory department, we work with two or three reference products and then carry the method over to the rest. We keep using existing processes and tools instead of building new ones. Workshops and interviews also work by video call, and each module can be commissioned on its own.
What to look for in a CRA service provider
Ask what you will actually have at the end: a document per product, a running SBOM chain, a documented reporting process. Results that go into the technical documentation can be verified.
Look for clear boundaries. Certificates in the conformity assessment procedure are issued by notified bodies, cybersecurity certificates by the certification bodies authorised for this; whoever advises you cannot issue either for your product. Legal services may only be provided by those authorised to do so. Also ask whether the provider works in your development environment and hands the result over to your team.
What we do not do
So that expectations are right from the start:
- We do not provide legal services. Where a question needs a legal decision, such as scope, role or product class, we supply the technical basis and flag it for review by your legal department or counsel.
- We are not a notified body, do not issue certificates and do not sign a declaration of conformity on your behalf.
- You submit Article 14 notifications yourself; we prepare the process, roles and templates.
- Penetration testing is not part of our services.
The CRA obligations remain with your company. We help you meet them and document the evidence.
Frequently asked questions
Where should we start?+
With the initial assessment and gap analysis. It records your products, gives a technical assessment of scope and role and shows where the gaps are. Only then can the remaining effort be planned reliably.
What does CRA consulting cost?+
Mainly it depends on the number of products and on how much evidence already exists. After a free initial call you receive a proposal with a clearly defined scope. Our article "What does CRA compliance cost?" gives an overview of the cost drivers.
We are ISO/IEC 27001 certified. Is that enough for the CRA?+
No. ISO 27001 describes a management system for the organisation, while the CRA sets requirements for the individual product and its life cycle. We take existing ISMS processes into account and only assess what is missing at product level.
Our process is certified to IEC 62443-4-1. What is left to do?+
That depends on what your process already delivers. We map Annex I Part I and Part II onto your existing practices and only assess the difference. A certified process evidences a method and, through SR-2, calls for a threat model per product. It does not by itself produce the risk assessment in the form Article 13(3) and (4) and Annex VII(3) require.
Do you work on site or remotely?+
Both. Document review, interviews and workshops work well by video call; with read access to code, build and documentation your teams need less interview time.
Do you submit the notifications to the CSIRT and ENISA?+
No. The manufacturer is obliged to report. We build the process, the roles and the templates with you so that you can meet the Article 14 deadlines.
Do you offer CRA implementation as a complete package?+
You can commission all modules together: gap analysis, risk assessment, SBOM and vulnerability management, reporting process, technical documentation and preparation of the conformity assessment, with a dedicated point of contact if you wish. Individual modules can be commissioned as well. You issue the declaration of conformity as the manufacturer.
How do I compare offers for CRA consulting?+
Compare what you will actually have at the end (a document per product, a running SBOM chain, a documented reporting process), whether product classification and the conformity assessment route are included, how the boundary to legal advice and notified bodies is described, and whether the provider works in your development environment. Totals alone say little if the scope is not comparable.
How is reliable security evidence for the CRA produced?+
From results that go into the technical documentation under Annex VII: the risk assessment per product, evidence for each Annex I requirement, the vulnerability handling processes including the SBOM and CVD policy, and test and examination reports. We build this documentation with your teams.
Further reading
- Does the CRA apply to my product?
- CRA product classes: default, class I, class II, critical
- CRA reporting: 24 hours, 72 hours, final report
- What does CRA compliance cost?
- Conformity assessment and CE marking
- The CRA for SMEs
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).
Last updated: 2026-10-09
Get in touch
Request CRA consulting
Tell us briefly about your products and your deadlines. The initial call is free and without obligation; we usually reply within one to two working days.