
Last updated: 2026-10-09
The Cyber Resilience Act (Regulation (EU) 2024/2847) has been in force since 10 December 2024. The first hard deadlines took effect on 11 September 2026: reporting obligations for actively exploited vulnerabilities and severe incidents. All product requirements apply to products placed on the market from 11 December 2027. The first question for every company is therefore: Am I subject to the CRA?
The answer depends on three factors: your role in the supply chain, the nature of your product, and the market on which you operate. This article walks you through the assessment steps systematically.
Step 1: What is your role in the supply chain?
The CRA addresses three distinct roles. Your obligations differ significantly depending on which role applies - so clarifying your role is the first and most important step.
Manufacturer
A manufacturer is any person who develops or has a product with digital elements developed and places it on the EU market under their own name or brand. It makes no difference whether the product is free of charge or sold commercially - freely available software also falls within scope if it is made available in the context of a commercial activity. Manufacturers bear the most extensive obligations: security by design, vulnerability handling, SBOM, technical documentation, CE marking, and reporting duties.
Importer
Importers are established in the EU and place products with digital elements on the Union market under the name or trademark of a manufacturer established outside the EU (Art. 3(16)). Before doing so they must ensure, among other things, that the manufacturer has carried out the conformity assessment and drawn up the technical documentation (Art. 19). An importer who places a non-compliant product on the market breaches its own obligations under the CRA.
Distributor
Distributors make products available on the EU market without making substantial modifications. Their obligations are lighter than those of manufacturers and importers. Before making a product available, however, they must verify, among other things, that the product bears the CE marking and that the manufacturer is identifiable.
Important: Anyone who relabels a product under their own name or makes substantial modifications is treated in law as a manufacturer - even if the original development took place elsewhere. This situation arises, for example, with white-label products and OEM arrangements.
Step 2: Is it a "product with digital elements"?
The CRA applies to products with digital elements - software and hardware products and their remote data processing solutions whose intended purpose or reasonably foreseeable use includes a direct or indirect logical or physical data connection to a device or network (Art. 2(1), Art. 3(1)).
This definition is intentionally broad. In particular, it covers:
- Proprietary software products (desktop, mobile, web applications) marketed as standalone products
- Embedded software and firmware in hardware products
- Network devices (routers, switches, firewalls)
- IoT devices with network connectivity
- Industrial control systems with digital interfaces
- Security products (VPN clients, antivirus software, password managers, PKI components)
- Remote data processing: processing at a distance whose software is designed and developed by or under the responsibility of the manufacturer and without which the product could not perform one of its functions (Art. 3(2)), for example the cloud back end of a device or an app
Pure SaaS services without a product-bound component do not fall directly within the CRA's scope - however, they may be captured as the remote data processing of a product. Hybrid offerings warrant careful delineation.
Step 3: Does an exception apply?
The CRA excludes certain products from its scope (Art. 2(2) to (7)), mainly those already covered by sector-specific rules:
- Medical devices under the MDR (Regulation (EU) 2017/745) and IVDR (Regulation (EU) 2017/746)
- Motor vehicles subject to the EU type-approval Regulation (EU) 2019/2144
- Aviation products certified under Regulation (EU) 2018/1139
- Marine equipment under Directive 2014/90/EU
- Spare parts that replace identical components and are manufactured to the same specifications
- Products developed or modified exclusively for national security or defence purposes, and products specifically designed to process classified information
If your product falls under one of these exclusions, the CRA does not apply to it; for sector-regulated products, the cybersecurity requirements follow the relevant sector law. However, if you develop software products sold to regulated industries but not themselves covered by sector regulation, the CRA remains applicable in principle.
Open-source software considerations
Open-source software stewards are legal persons that are not manufacturers and that systematically provide sustained support for the development of free and open-source software intended for commercial activities (Art. 3(14)), such as foundations. They are exempt under Article 64(10)(b) from the fines in paragraphs 3 to 9. Whether this also covers infringements of the reporting obligation (paragraph 2) is not clear from the wording; recital 120 points that way. Companies that integrate open-source components into their own products and market those products commercially have the obligations of a manufacturer of those products, including vulnerability handling for the integrated components.
Considerations for micro and small enterprises
The CRA contains no general size-based exemption: SMEs are subject to the same requirements as large enterprises. Micro and small enterprises benefit from targeted relief, for example the option to submit the technical documentation in a simplified format, with the form to be set by the Commission (Article 33(5)), and an exception from fines for a missed 24-hour early warning (Article 64(10)), whose scope is a question of interpretation. The reporting obligation itself applies regardless of company size. The essential product requirements apply to them as well. For concrete action steps tailored to mid-sized companies, see our CRA page for SMEs.
Step 4: A systematic assessment framework
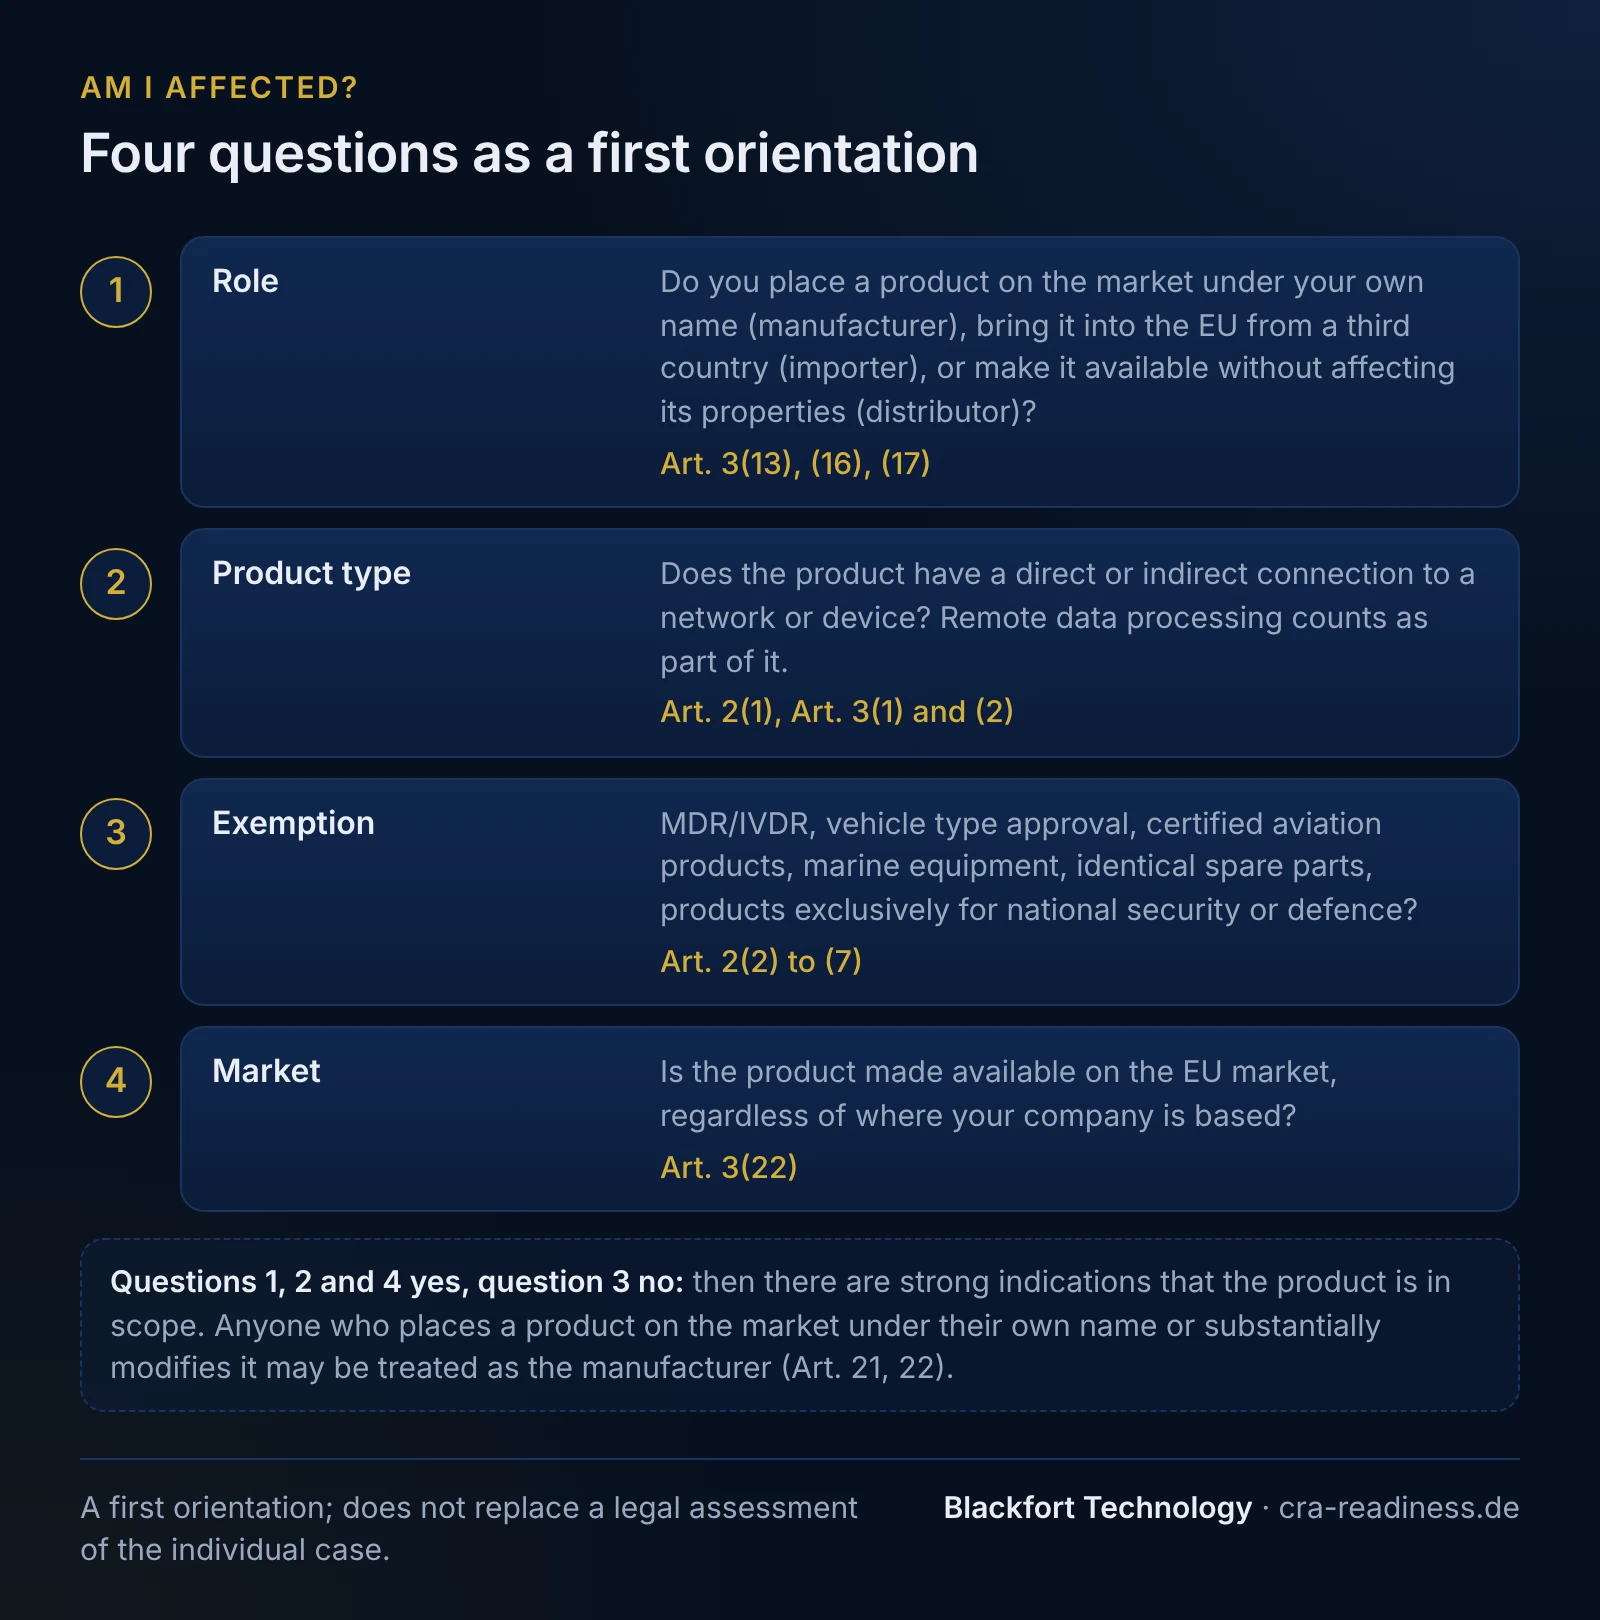
The following four questions provide a rapid orientation framework. They give a first orientation and do not replace a legal assessment of your individual situation.
- Role: Are you placing a product on the EU market under your own name, importing a product from a third country into the EU, or making a product available without substantially modifying it?
- Product type: Does your product have a direct or indirect connection to a network or another device?
- Exception: Does your product fall under an exclusion in Art. 2(2) to (7) (e.g. MDR, IVDR, vehicle type-approval, certified aviation products, marine equipment, spare parts, national security and defence)?
- Market: Is the product made available on the EU market - regardless of where your company is established?
If you answer Yes to questions 1, 2, and 4, and No to question 3, it is likely that your product falls within the scope of the CRA. For a more granular assessment of your specific situation, you can use our interactive CRA check.
What follows from being in scope?
Once it is established that the CRA applies to your product, the specific obligations depend on the product class. The CRA distinguishes:
- Default products - self-assessment by the manufacturer (Module A)
- Important products Class I (Annex III) - self-assessment (Module A) only with full application of harmonised standards, common specifications or a European cybersecurity certification scheme (at least “substantial”); otherwise third-party assessment by a notified body (Module B+C or H)
- Important products Class II (Annex III) - third-party assessment always, no self-assessment: Module B+C or H with a notified body or, where available, a European cybersecurity certificate at least at assurance level “substantial” (Art. 32(3))
- Critical products (Annex IV) - a European cybersecurity certificate mandated by delegated act (Art. 8(1)), otherwise the Class II procedures (Art. 32(4))
A detailed explanation of product classes and the corresponding conformity assessment procedures is available in the article CRA Product Classes: Default, Class I/II and Critical.
The first hard deadline: in force since September 2026
Regardless of product class, all affected manufacturers have been subject to reporting obligations since 11 September 2026: actively exploited vulnerabilities and severe incidents must be reported without undue delay and in any event within 24 hours of becoming aware as an early warning, and without undue delay and at the latest within 72 hours as a notification. A final report follows no later than 14 days after a corrective or mitigating measure is available (vulnerabilities) or within one month of the notification (severe incidents). Reports are submitted via ENISA's Single Reporting Platform (SRP); they go through the endpoint of the CSIRT designated as coordinator and are simultaneously accessible to ENISA.
This means that even though full product requirements only apply from late 2027, the necessary processes and internal structures (PSIRT, escalation paths, documentation requirements) must already be in place today, as the reporting obligation has applied since September 2026. Full details on timelines and operational requirements are available in the article CRA Reporting Obligations since 11 September 2026.
Scope confirmed - what next?
The next step after confirming that the CRA applies is a structured gap analysis: where does your product stand today relative to CRA requirements - in security by design, vulnerability handling, SBOM, and technical documentation? The SBOM obligation in particular needs more lead time than it first appears. Detailed requirements and format specifications (CycloneDX, SPDX, TR-03183-2) are explained in the article SBOM Requirements under the CRA.
Blackfort Technology supports manufacturers of digital products in structured CRA preparation - from scope analysis and gap assessment through to the implementation of reporting processes and SBOM infrastructure. Blackfort Technology brings hands-on implementation experience from PKI, DORA, NIS2 and ISMS engagements.
All CRA obligations at a glance - or go straight to the interactive CRA check.
Frequently asked questions
Does the Cyber Resilience Act apply to free software?+
I only sell in Germany - does the CRA still apply?+
We manufacture medical devices - are we exempt from the CRA?+
What exactly is a 'product with digital elements'?+
Does the CRA apply to importers selling US software licences?+
Since when have the first CRA obligations applied?+
Sources
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).