
Last updated: 2026-10-09
The Cyber Resilience Act (Regulation (EU) 2024/2847) requires cyber-secure products with digital elements and backs these obligations with a tiered penalty framework. That framework sits in Article 64 and defines maximum amounts for infringements. Understanding the order of magnitude of possible fines helps you weigh the cost of CRA compliance in commercial terms. This article frames the rules in technical-organisational terms; it is not legal advice.
The core principle: “up to” and “whichever is higher”
Article 64 works with three penalty tiers. Each tier states both an absolute euro amount and a percentage of the total worldwide annual turnover of the preceding financial year. A fine may be imposed of up to the higher of the two figures. For high-revenue groups the percentage therefore acts as the ceiling; for smaller firms the fixed euro amount does. These are maxima - the actual amount is set by the competent authorities on a proportionate, case-by-case basis.
The reference base matters: the percentage is measured against a company's total worldwide turnover, not against revenue from the product concerned. In group structures this can amount to substantial sums. At the same time the Regulation requires penalties to be effective, proportionate and dissuasive (Art. 64(1)). The maxima set the upper frame. Within it, the authority takes all circumstances of the case into account, in particular the nature, gravity, duration and consequences of the infringement, previous fines for similar infringements and the size and market share of the company (Art. 64(5)).
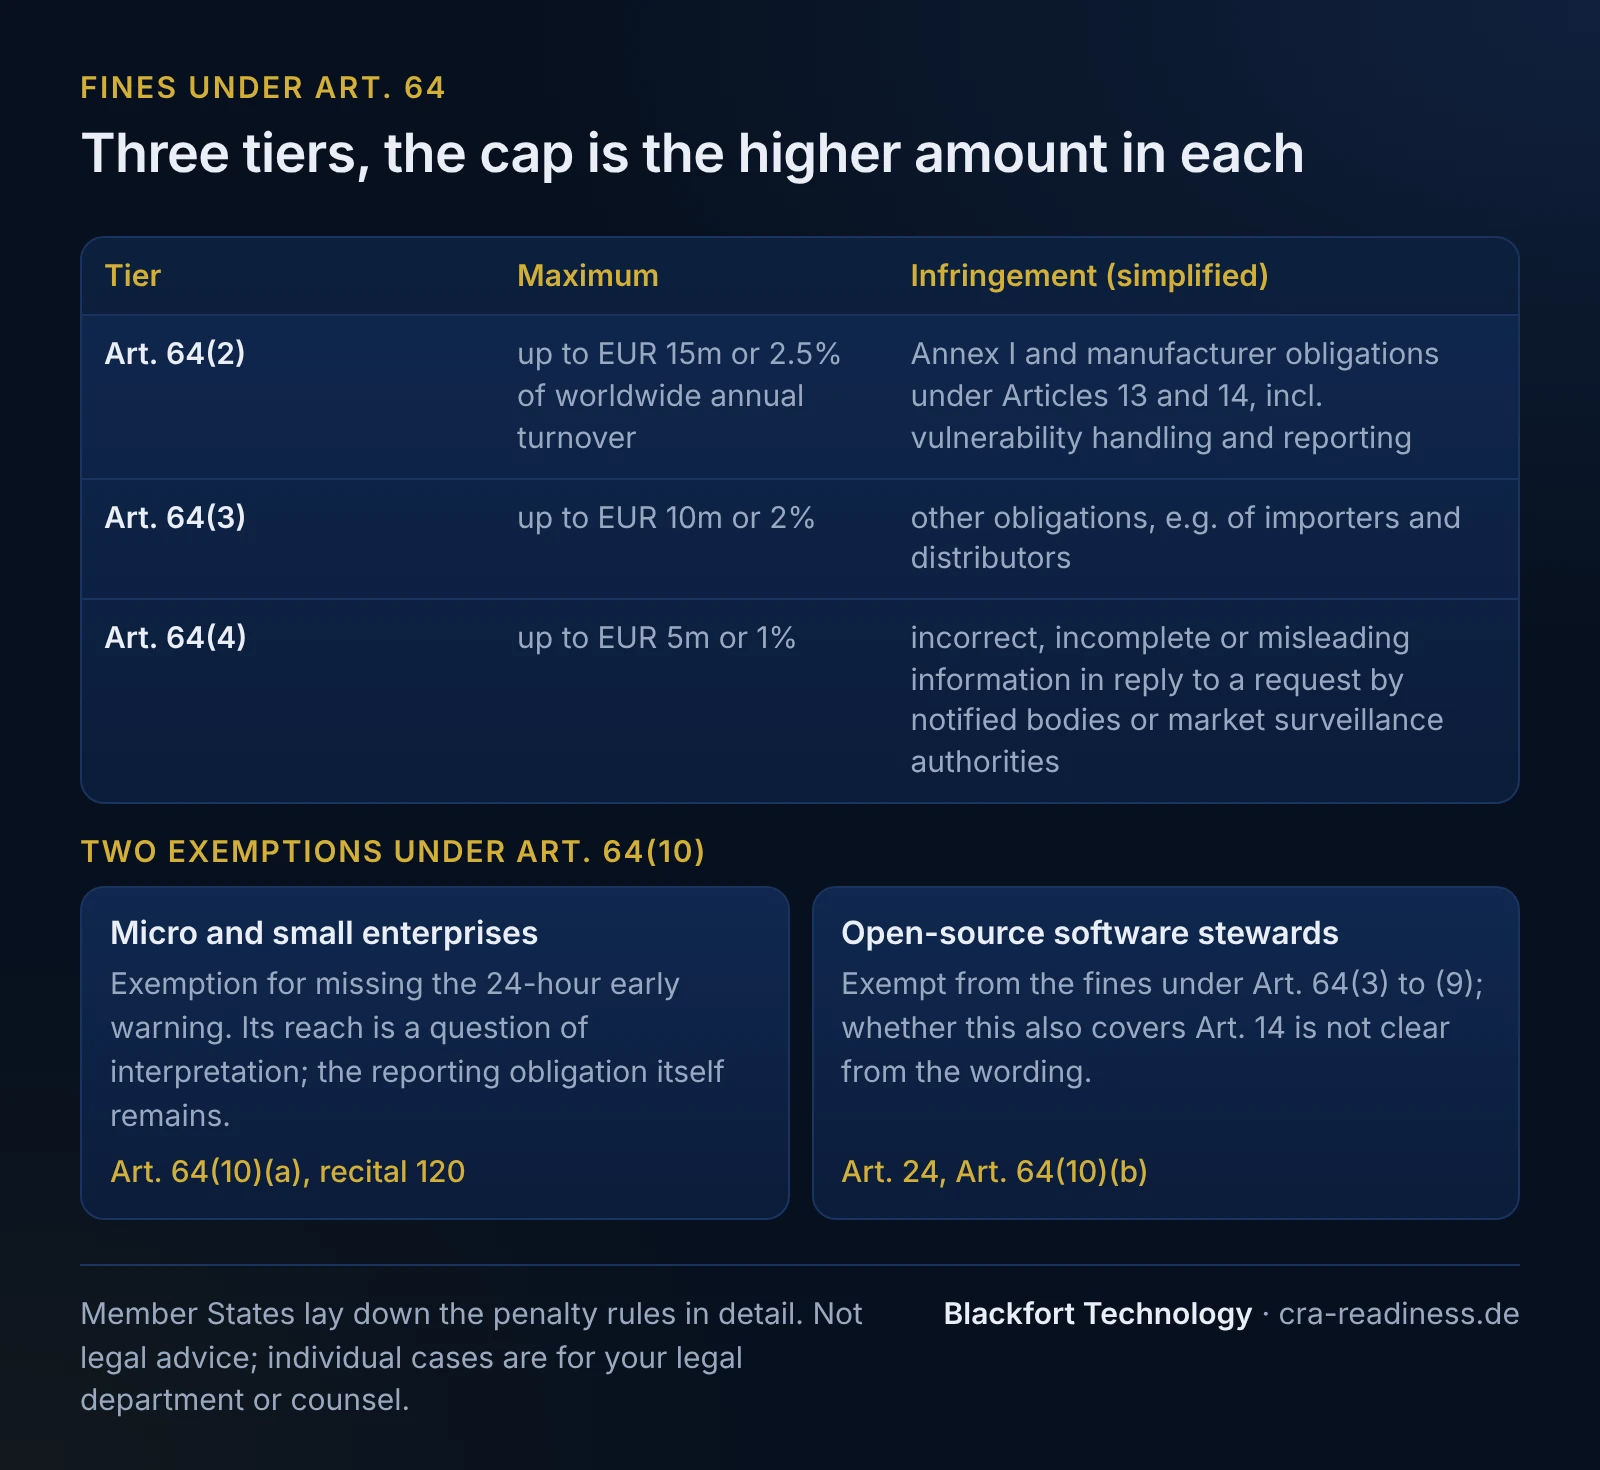
The three penalty tiers at a glance
| Maximum (whichever is higher) | For what (simplified) |
|---|---|
| up to €15,000,000 or 2.5% of worldwide annual turnover | Infringement of the essential requirements in Annex I and of the manufacturer obligations in Articles 13 and 14 (incl. vulnerability handling and reporting duties). |
| up to €10,000,000 or 2% of worldwide annual turnover | Infringement of other obligations - for example the duties of importers and distributors and conformity-related duties. |
| up to €5,000,000 or 1% of worldwide annual turnover | Supplying incorrect, incomplete or misleading information to notified bodies or market surveillance authorities. |
Key point: The most serious infringements - against the product's own security requirements and against vulnerability handling and reporting - sit in the top tier. If you want to establish whether and how your product is affected at all, start with the applicability assessment.
Why this is not the GDPR
It is a misconception to transfer the figures familiar from the General Data Protection Regulation (up to €20m or 4% of group turnover) straight onto the CRA. That is wrong. The CRA has its own, lower ceiling: the top tier is €15m or 2.5%, not €20m or 4%. The percentage refers, as under the GDPR, to worldwide annual turnover, but the rates are markedly lower. Both regimes can apply side by side where a situation touches both product security and personal data - they do not replace one another.
Who enforces? The market surveillance authorities
Enforcement of the CRA rests with the Member States' market surveillance authorities. They monitor products with digital elements on the market, can request conformity evidence, technical documentation and information, order corrective measures up to withdrawal or recall, and impose fines. In Germany the concrete allocation of authority is a matter for the German implementing act; the government draft (Bundestag printed paper 21/6134) has not yet been adopted (as of 9 October 2026). The practical consequence for companies: providing reliable, complete and correct information to these authorities is itself an obligation subject to penalties - the third tier (up to €5m / 1%) targets precisely incorrect or misleading statements.
Two important carve-outs
Microenterprises and small enterprises
Article 64(10) provides an exception for manufacturers that qualify as microenterprises or small enterprises with regard to missing the early warning deadline in Article 14(2)(a) or Article 14(4)(a). By its wording, however, paragraph 10 derogates only from paragraphs 3 to 9, while infringements of Article 14 fall under paragraph 2. Recital 120 assumes that no fines are imposed in this case. The scope of the exception is a question of interpretation. The 72-hour notification and the final report are not covered by paragraph 10, and the reporting obligation itself remains in any case.
Open-source software stewards
The CRA recognises a distinct, lighter-touch role for open-source software stewards (Article 24). These are legal persons that systematically support the development of free and open-source software for commercial purposes without themselves being manufacturers. A regime with reduced obligations applies to them. Article 64(10)(b) exempts them from the fines in paragraphs 3 to 9 for any infringement of the Regulation. Under Article 24(3), however, obligations from Article 14 also apply to stewards (paragraph 1 to the extent that they are involved in the development of the products, and, for severe incidents affecting their development infrastructure, paragraphs 3 and 8), and infringements of Article 14 are subject to fines under paragraph 2, to which paragraph 10 does not refer. Whether the exemption also covers these is not clear from the wording. Recital 120 assumes that no fines are imposed on stewards and points that way. In individual cases, your legal department or a law firm should clarify this. Individual, non-commercial open-source contributors fall outside the scope in any case. The underlying idea: someone who supports free software in a fostering role, without placing it on the market as a product in their own name, should not be subject to the full obligations and penalty framework of a manufacturer.
Not just fines: the actual enforcement toolkit
The fines in Article 64 are only one part of the enforcement picture. Market surveillance authorities can additionally order a non-conforming product to be withdrawn from the market or recalled, restrict or prohibit its further distribution, and compel corrective measures. In commercial terms, the threatened distribution halt or recall can weigh more heavily than the fine itself - it hits revenue directly and can entail reputational damage. The penalty tiers should therefore be read together with this overall toolkit.
What does this mean for your preparation?
The penalty tiers reveal where the Regulation places its greatest weight: on the essential security requirements and on vulnerability handling and reporting. These areas need organisational lead time. Because the obligations enter into application in a staggered manner and the penalties only bite once the respective obligation applies, it is worth looking at the CRA deadlines and timeline. Investing in conformity processes today reduces the fine risk and the risk of an ordered market withdrawal, which can weigh more heavily in business terms than the fine itself.
- Essential requirements (Annex I) and vulnerability handling/reporting (Art. 13/14) are the costliest infringements - start here.
- Information to authorities must be correct and complete - that too is penalised.
- Micro/small enterprises: Article 64(10) provides an exception for a missed 24-hour early warning (Art. 14(2)(a) / (4)(a)); its scope is a question of interpretation. The 72-hour notification and the final report are not covered, the obligation remains.
- Open-source stewards: Article 64(10)(b) exempts them from the fines in paragraphs 3 to 9. Whether this also covers infringements of the reporting obligations in Article 14 (paragraph 2) is not clear from the wording; recital 120 points that way.
For an overview of the Regulation as a whole, see our introduction to the Cyber Resilience Act.
Frequently asked questions
How high can CRA fines go at most?+
Are CRA fines as high as under the GDPR?+
Are there exemptions for small companies?+
Can open-source stewards be fined?+
Who imposes the fines and when do they apply?+
Sources
- Regulation (EU) 2024/2847 (Cyber Resilience Act), official text - Article 64
- European Commission - Cyber Resilience Act summary
- BSI - Cyber Resilience Act (information for companies and organisations)
- Official Journal of the EU - CRA full text (PDF)
- Bundestag printed paper 21/6134: German government bill implementing the CRA (PDF, German)
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).