
Last updated: 2026-10-09
The EU Cyber Resilience Act (CRA, Regulation (EU) 2024/2847) places duties on manufacturers and also on the actors further down the supply chain. The distributor - in CRA terms whoever makes available on the market a product with digital elements without affecting its properties, without being the manufacturer or importer (Art. 3(17)) - carries a distinct, clearly defined responsibility. This page provides a technical-organisational orientation on distributor duties under Art. 20. It offers guidance, not binding individual advice; a legal assessment remains reserved for legal counsel.
The key point up front
The distributor is a gatekeeper, but a lighter one than the importer. It acts with due care in relation to the requirements of the CRA: it verifies that the CE marking is present and that the manufacturer and importer have met their marking and information duties. It does not create product security itself, draw up technical documentation or carry out a conformity assessment. Even so, its role is a genuine control function; Article 64(3) provides for fines for infringements of Article 20.
Who is a “distributor” under the CRA?
A distributor is an actor in the supply chain that makes available on the market - offers, supplies or resells - a product with digital elements without affecting its properties, while being neither the manufacturer nor the importer. Typical examples are specialist retailers, system houses, distributors, resellers or online-marketplace sellers who pass on finished products that have already been placed on the market. Note: the distributor receives a product that someone else developed and yet another party may have imported. Its task is to prevent a product from reaching the market through it where, on the basis of the information in its possession, it has reason to believe the product is non-conforming.
The due-care duty (Art. 20) in detail
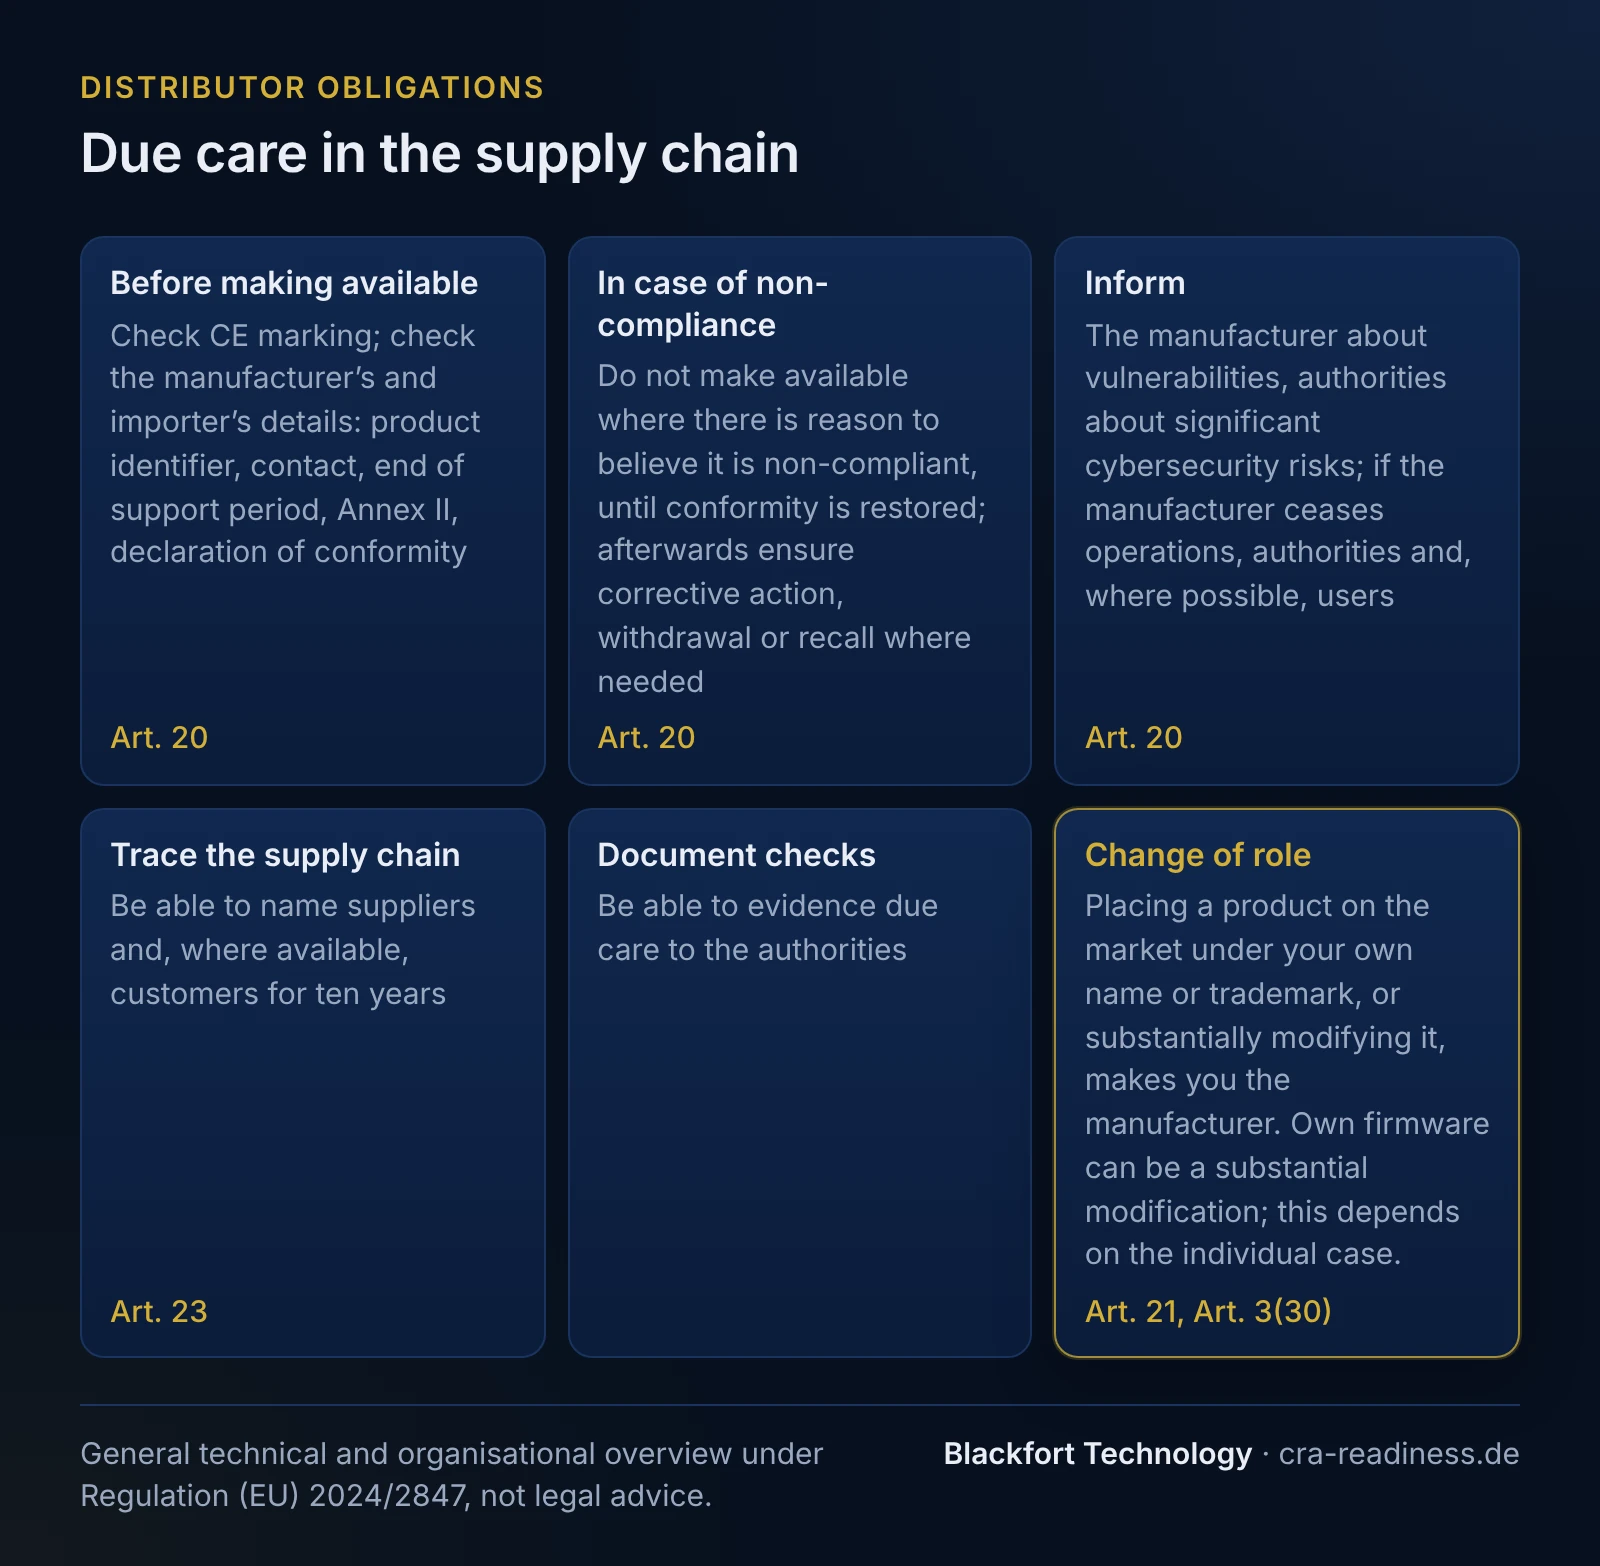
The central yardstick is due care (Art. 20(1)). Before making a product available, the distributor verifies (Art. 20(2)):
- CE marking present: Does the product bear the CE marking? It is the visible signal that the manufacturer has declared conformity.
- Information from manufacturer and importer: type, batch or serial number, the manufacturer's name and contact details, the end date of the support period (at least month and year) and, where an importer was involved, the importer's contact details (Art. 13(15), (16) and (19), Art. 19(4)).
- Accompanying documents: Are the user information and instructions under Annex II and the EU declaration of conformity or the simplified EU declaration of conformity supplied (Art. 13(18) and (20)), and have the manufacturer or importer provided all necessary documents to the distributor?
The verification depth is deliberately lower than the importer's. The importer (Art. 19) ensures that the conformity assessment was carried out and the technical documentation drawn up; the distributor checks the presence of the outward conformity markers and the accompanying documents. It is a due-care and plausibility check, not a re-assessment of conformity.
Important: Where the distributor, on the basis of the information in its possession, has reason to believe that a product or the manufacturer's processes do not conform to the essential requirements in Annex I, it must not make the product available on the market until conformity has been established (Art. 20(3)). The due-care duty is therefore not a pure visual check - it bites as soon as there are concrete indications of non-conformity. Where the product poses a significant cybersecurity risk, it also informs the manufacturer and the market surveillance authorities without undue delay.
Non-conforming products: do not make available
The second core duty is a prohibition: a product that the distributor knows or must assume to be non-conforming must not be made available on the market. Where non-conformity comes to light only after the product has been made available, the distributor makes sure that the necessary corrective action is taken - from bringing the product into conformity to, where necessary, withdrawal or recall (Art. 20(4)). Here too: the distributor initiates and cooperates in corrections; the substantive rectification of the product rests with the manufacturer.
Informing: manufacturer and authorities
The distributor is embedded in the information chain:
- Inform the manufacturer of vulnerabilities: Where the distributor becomes aware of a vulnerability in the product, it informs the manufacturer without undue delay (Art. 20(4)).
- Inform authorities of significant risk: Where a product presents a significant cybersecurity risk, it immediately informs the market surveillance authorities of the Member States in which it made the product available, giving details in particular of the non-compliance and of any corrective action taken.
- Information and cooperation: On a reasoned request it provides the market surveillance authority with the information and documentation demonstrating conformity and cooperates with it (Art. 20(5)).
- Manufacturer ceases operations: Where the distributor becomes aware that the manufacturer has ceased its operations and can no longer meet its obligations, it informs the market surveillance authorities without undue delay and, where possible, the users (Art. 20(6)).
The distributor has no reporting obligation under Art. 14; the deadlines for early warning, notification and final report via the single reporting platform apply to the manufacturer. The distributor may report vulnerabilities and incidents voluntarily under Art. 15. In addition, it must be able to tell the authorities on request, for ten years, from whom it obtained a product and, where available, to whom it supplied it (Art. 23).
Role change: when the distributor becomes a manufacturer
A pitfall: A distributor or importer that places a product on the market under its own name or trademark, or substantially modifies a product already placed on the market, is considered a manufacturer and is subject to the obligations of Articles 13 and 14 (Art. 21): essential requirements, vulnerability handling, technical documentation, conformity assessment, EU Declaration of Conformity, CE marking, reporting. A distributor can thus unintentionally slip into the manufacturer role - for example by re-labelling, rebranding or loading its own firmware. As a rule of thumb: once you market a product as your own or substantially modify it, you are no longer merely a gatekeeper. Whether a specific modification is “substantial” (Art. 3(30)) is a question for the individual case.
Distributor duties checklist
The following checklist summarises the distributor's duties under Art. 20 and Art. 23 in practical terms:
- Verify the CE marking - is it present on the product?
- Verify the information and documents from manufacturer and importer - product identifier, contact details, end date of the support period, user information under Annex II, EU Declaration of Conformity.
- Do not make available when in doubt - where there is reason to believe non-conformity, keep the product off the market.
- Make sure corrective action is taken - where non-conformity is later identified (bring into conformity, withdraw/recall if needed).
- Inform the manufacturer of vulnerabilities - without undue delay once a vulnerability becomes known.
- Inform market surveillance authorities of significant cybersecurity risk - including details of non-compliance and corrective action.
- Manufacturer ceases operations - inform the market surveillance authorities and, where possible, users without undue delay.
- Be able to trace the supply chain for ten years - name suppliers and, where available, customers (Art. 23).
- Keep an eye on the role change - do not become a manufacturer unnoticed through rebranding or substantial modification.
- Document the verification steps - record due care so it can be demonstrated to the authorities.
In perspective: lighter than the importer, but real
The distributor role is deliberately lighter than the importer's - the distributor verifies less deeply and has none of the original manufacturer duties. But “lighter” does not mean “without consequences”: the due-care duty, the prohibition on making non-conforming products available, and the information duties are genuine control obligations whose breach can lead to market-surveillance measures and fines under Art. 64(3). For how the roles interlock, see our overview of the CRA roles; the markedly more verification-intensive neighbouring role is covered in our page on the importer duties. The applicability check gives a first orientation on whether your product is affected.
Note: These explanations are general technical-organisational information, not legal advice within the meaning of the German Legal Services Act (RDG). The allocation of roles and the resulting duties depend on the individual case and may be further specified by Commission guidance.
Frequently asked questions
What does a distributor owe under the CRA?+
Must a distributor re-assess a product's CRA conformity itself?+
How does the distributor differ from the importer under the CRA?+
What must a distributor do if the manufacturer ceases operations?+
Can a distributor become a manufacturer through rebranding?+
Sources
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).