
Last updated: 2026-10-09
Connected products with digital elements - from smart locks and routers to wearables and industrial controllers - fall, in principle, within the scope of the Cyber Resilience Act (Regulation (EU) 2024/2847). The condition is that their intended purpose or reasonably foreseeable use includes a direct or indirect logical or physical data connection to a device or network (Art. 2(1), Art. 3(1)). For makers of IoT and embedded products this means: cybersecurity becomes a prerequisite for CE marking and therefore for access to the EU market. This page offers technical-organisational orientation - not legal advice.
Transition: Delegated Regulation (EU) 2022/30 (RED) and the CRA
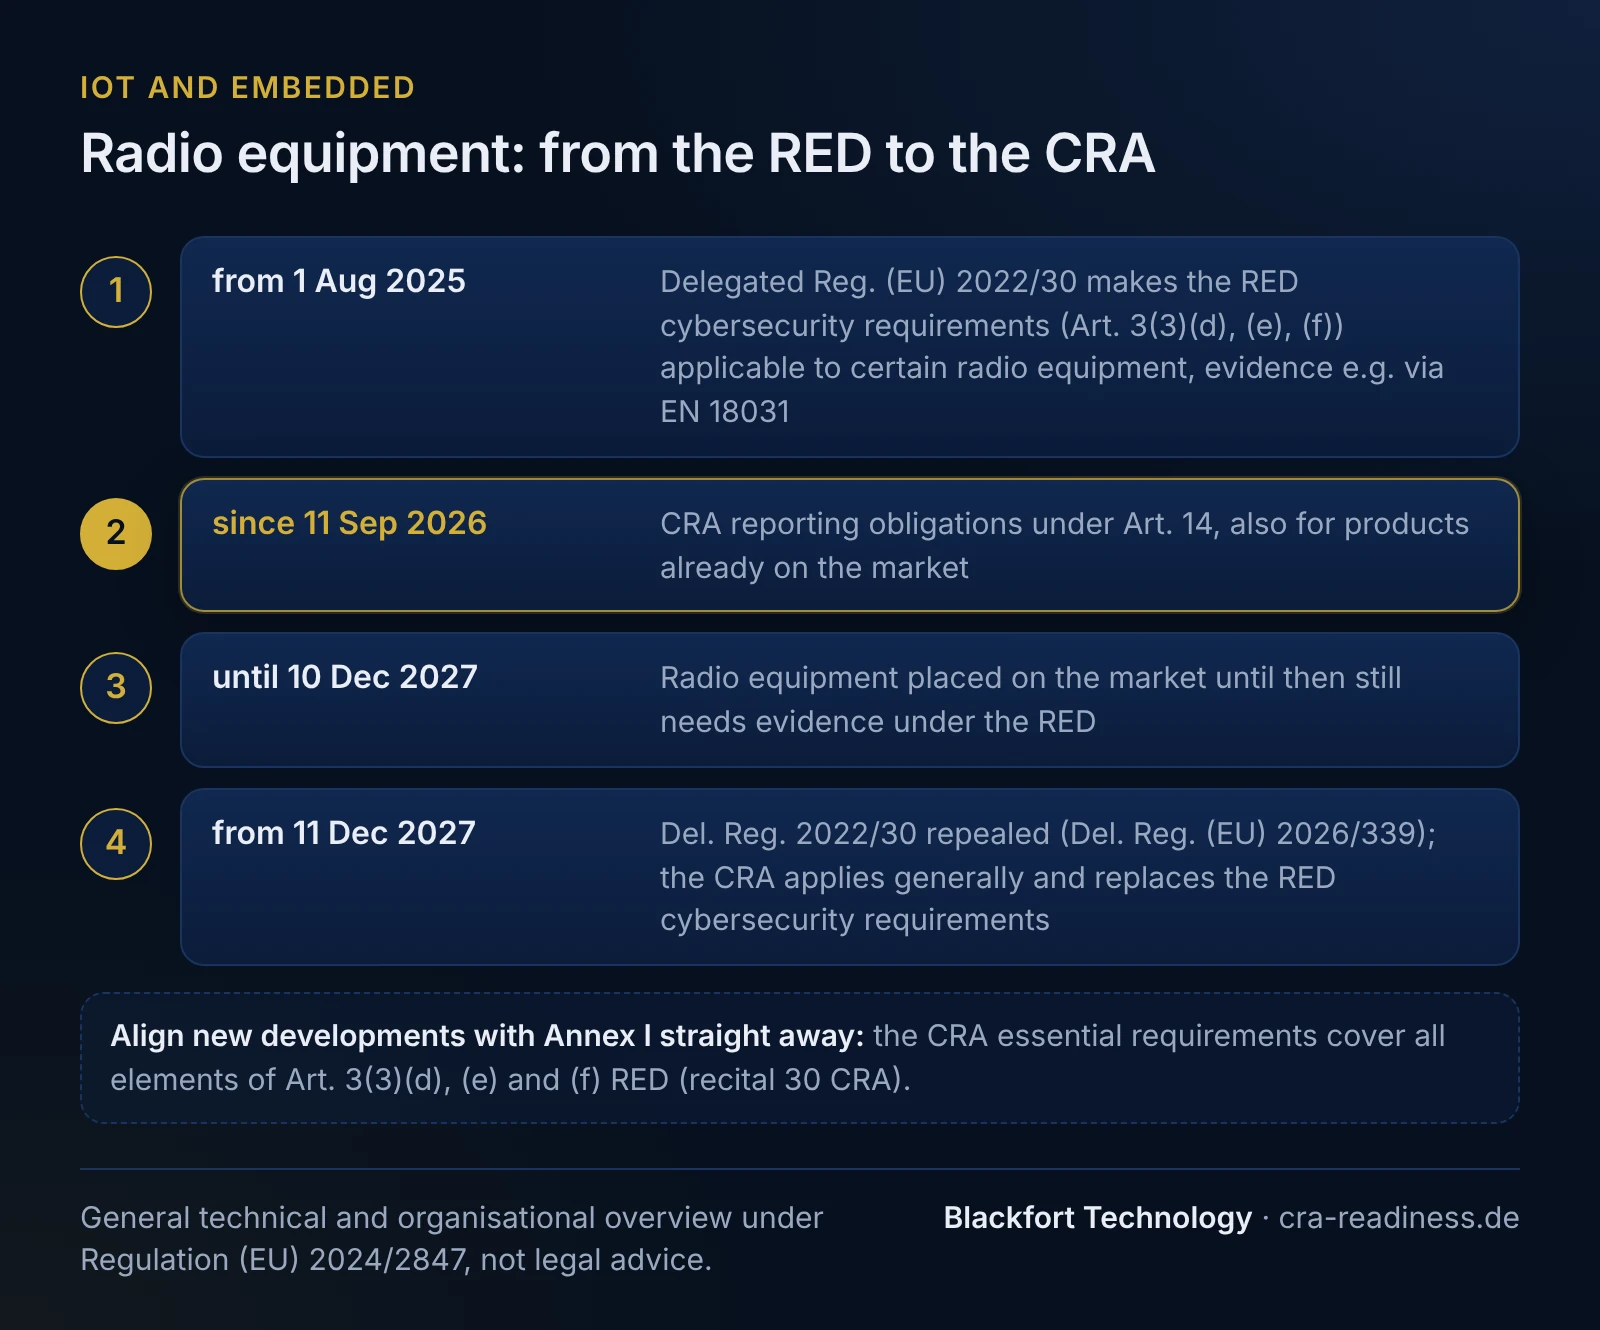
For radio equipment there is a transition window between the Radio Equipment Directive and the CRA. Delegated Regulation (EU) 2022/30 makes the cybersecurity requirements of the Radio Equipment Directive (RED, Article 3(3)(d), (e) and (f) of Directive 2014/53/EU) applicable to certain radio equipment. It applies from 1 August 2025 and, under Article 1 of Delegated Regulation (EU) 2026/339, is repealed with effect from 11 December 2027, the day from which the CRA applies in general.
This creates a transition window from 1 August 2025 to 10 December 2027: during that period the RED cybersecurity requirements apply to radio equipment, after which the CRA replaces them. For radio equipment placed on the market in this period, market surveillance and conformity checks under the RED are not affected by the repeal (recital 5 of Delegated Regulation (EU) 2026/339). Because the CRA’s essential requirements cover all elements of Article 3(3)(d), (e) and (f) RED (recital 30 CRA), it is worth aligning new developments with Annex I CRA straight away. Radio equipment placed on the market up to 10 December 2027 still needs the evidence under the Radio Equipment Directive, for example via EN 18031. More on this on our page on EN 18031 and the Radio Equipment Directive.
Are your products affected?
A “product with digital elements” (PDE) is any software or hardware product together with its remote data processing solutions (Art. 3(1)). Cloud or back-end processing also counts where the manufacturer has designed and developed its software, or had it designed and developed under its responsibility, and the product could not perform one of its functions without it (remote data processing, Art. 3(2)). Excluded are, among others, medical devices and in-vitro diagnostics (MDR/IVDR), products within the scope of the motor vehicle type-approval Regulation (EU) 2019/2144 and aviation products certified under Regulation (EU) 2018/1139 (Art. 2(2) and (3)). For products under other sectoral rules, the Commission may limit or exclude application by delegated act (Art. 2(5)). A purely standalone SaaS or cloud application is in principle outside the CRA; the NIS2 Directive covers cloud computing services, as a rule only where the provider is at least a medium-sized enterprise (recital 12 CRA). The boundary is not always clear-cut at the edges.
Our CRA applicability check gives a first orientation per product.
Product classes: how strictly is conformity assessed?
The CRA has four tiers (Art. 32, Annexes III/IV). The classification determines the conformity route. It is schematically to be understood as follows - when in doubt, classify conservatively and have it reviewed:
Default (unclassified)
All products not listed in Annex III or IV: self-assessment (Module A). No notified body required.
Important - Class I (Annex III)
Connected consumer and industrial products can land here, e.g. smart-home assistants, smart locks/cameras/alarms, connected toys, health wearables, routers/modems/switches, microcontrollers with security functions. Self-assessment (Module A) only if harmonised standards, common specifications or a European cybersecurity certification scheme (assurance level at least “substantial”) are fully applied - otherwise third-party assessment (Module B+C or H).
Important - Class II (Annex III)
E.g. firewalls, IDS/IPS and tamper-resistant micro-processors/-controllers. Third-party assessment is always required here (Modules B and C, Module H or a European cybersecurity certification scheme at assurance level at least “substantial”); no self-assessment.
Critical (Annex IV)
E.g. secure elements, smart-meter gateways, HSMs. A European certification scheme (at least “substantial”) once a delegated act under Art. 8(1) requires it; otherwise the Class II routes.
For orientation: third-party assessment is required in every case for Class II and critical products, and for Class I whenever harmonised standards, common specifications or a European scheme are not applied in full. Default-category products self-assess. Details on classification are available under CRA product classes. The technical category descriptions are set out in Commission Implementing Regulation (EU) 2025/2392.
Core duties & action areas for IoT makers
From Annex I and the manufacturer duties (Art. 13/14), the following action areas are particularly relevant for connected products:
- Secure default configuration: ship with secure defaults (security-by-default), no hard-wired default passwords, minimised attack surface.
- Secure, free updates: disseminate security updates without delay and free of charge (a different arrangement is possible with business users for tailor-made products); separate security from feature updates where feasible; secure update distribution.
- Support period: set so that it reflects the expected time of use, at least 5 years (shorter only where the expected use is shorter). For long-lived embedded devices, plan this early into roadmap and BOM.
- Vulnerability handling incl. SBOM: identify and document vulnerabilities and components - including an SBOM in a commonly used, machine-readable format, at least for top-level dependencies. The Regulation mandates no specific format. Examples of machine-readable formats are CycloneDX and SPDX (ISO/IEC 5962); what counts for the requirement is the content, at least the top-level dependencies.
- CVD policy: a mandatory coordinated-vulnerability-disclosure policy including a contact address for reporting.
- Technical documentation (Annex VII) & CE: architecture, SBOM, CVD policy, update distribution, risk assessment mapped to Annex I; EU Declaration of Conformity (Art. 28), CE marking (Art. 30). Retention at least 10 years or for the support period, whichever is longer.
- Reporting duties (Art. 14): report actively exploited vulnerabilities and severe incidents having an impact on the security of the product to the CSIRT designated as coordinator and to ENISA: early warning without undue delay and in any event within 24 hours, notification within 72 hours, final report no later than 14 days after a corrective or mitigating measure is available (vulnerabilities) or one month after the notification (incidents).
Timeline: these deadlines apply
| Date | What applies |
|---|---|
| 10 December 2024 | CRA enters into force (no enforceable product duties yet). |
| 1 August 2025 | RED Delegated Regulation (EU) 2022/30 applies - cybersecurity for radio equipment (interim window begins). |
| 11 June 2026 | Notified-body provisions (Chapter IV) apply. |
| 11 September 2026 | Manufacturer reporting duties (Art. 14) - also for products already on the market. |
| 11 December 2027 | General application: Annex I requirements, conformity assessment, CE marking. Delegated Regulation (EU) 2022/30 is repealed with effect from this day (Delegated Regulation (EU) 2026/339). |
Recommended roadmap: (1) classify the product portfolio and clarify applicability; (2) gap analysis against Annex I; (3) set up an SBOM pipeline and CVD policy; (4) establish update and support processes for the whole support period (at least 5 years); (5) prepare technical documentation and the conformity route. Aligning radio equipment with Annex I CRA today while evidencing RED compliance via EN 18031 lets you reuse the risk assessment and documentation as a starting point in 2027.
Background and overview: Cyber Resilience Act.
Frequently asked questions
Do my IoT devices really fall under the CRA?+
What does RED Regulation (EU) 2022/30 mean for me?+
Do I need a notified body for my smart product?+
Which SBOM format does the CRA mandate?+
From when must I be compliant and what happens on breach?+
Sources
- Regulation (EU) 2024/2847 (Cyber Resilience Act) - EUR-Lex
- European Commission - Cyber Resilience Act summary
- BSI - Cyber Resilience Act
- Official Journal of the EU - CRA full text (PDF)
- Delegated Regulation (EU) 2022/30 (RED DA, cybersecurity of radio equipment)
- Delegated Regulation (EU) 2026/339 (repealing Delegated Regulation (EU) 2022/30)
This content provides general technical and organizational information on the Cyber Resilience Act (Regulation (EU) 2024/2847) and does not constitute legal advice (no legal services within the meaning of the German RDG).